The PHP2Shell flaws have reached the remote maintenance layer of operational technology (OT). On 10 November 2026, CERT@VDE, the German coordination center for industrial vendors, published five advisories covering remote access portals from MB connect line and Helmholz, and industrial routers from Weidmueller and ads-tec. These are the systems machine builders and integrators use to reach programmable logic controllers (PLCs) and human-machine interfaces (HMIs) in the field. The two PHP2Shell flaws, CVE-2026-109618 and CVE-2026-109619, are already on the Known Exploited Vulnerabilities (KEV) catalog of the Cybersecurity and Infrastructure Security Agency (CISA).
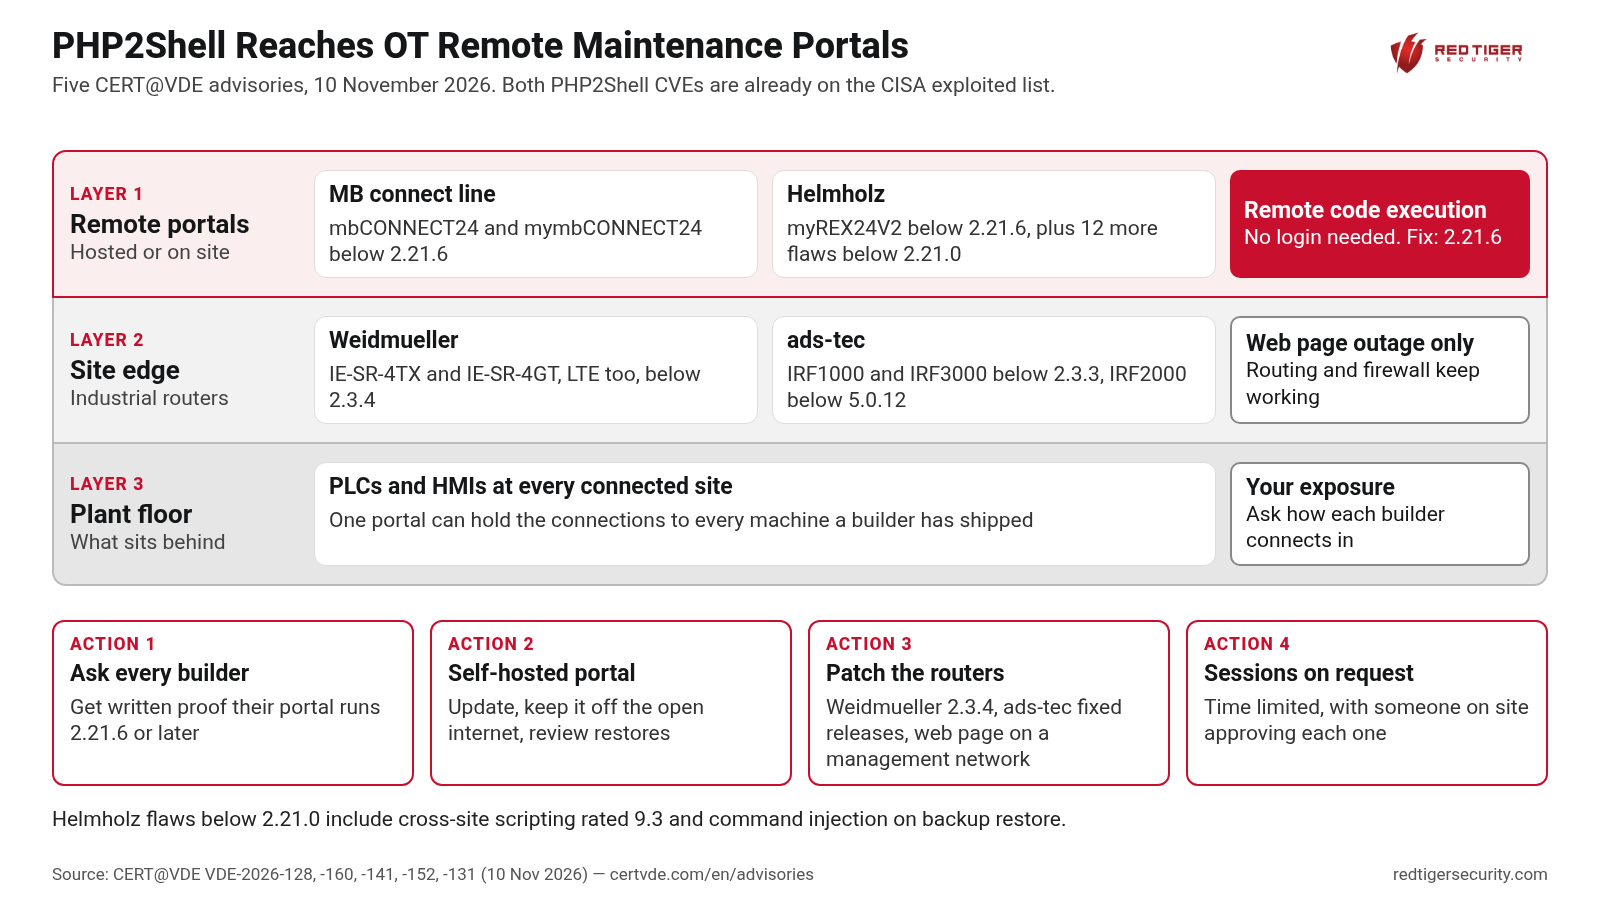
VDE-2026-128 covers MB connect line mbCONNECT24 and mymbCONNECT24 below version 2.21.6. MB connect line says both PHP2Shell flaws can lead to unauthenticated remote code execution, with a total loss of confidentiality, integrity and availability. The fix is version 2.21.6.
VDE-2026-160 covers the same PHP2Shell issue in Helmholz myREX24V2 and myREX24V2.virtual below 2.21.6. The fix is 2.21.6.
VDE-2026-141 adds twelve more flaws in myREX24V2 and myREX24V2.virtual below 2.21.0, CVE-2026-60035 through CVE-2026-60046. They include cross-site scripting rated 9.3 and cross-site request forgery rated 8.1 that let an outside attacker trick a logged-in user into shutting down the server or restoring an uploaded backup, password resets with no rate limit, a fixed backup password and command injection when a backup is restored.
A portal like this holds the connection to every machine a builder supports. If the portal falls, every site behind it is exposed.
VDE-2026-152 covers Weidmueller IE-SR-4TX and IE-SR-4GT security routers, including the LTE models, below firmware 2.3.4. Only CVE-2026-109618 applies, and in this configuration it can only make the web interface temporarily unavailable. Routing and firewall functions are not affected. The fix is 2.3.4.
VDE-2026-131 covers ads-tec IRF1000 and IRF3000 routers below 2.3.3, IRF2000 below 5.0.12 and certain web terminals, again with web interface impact only. Fixed firmware is available.
Prior Red Tiger advisories on PHP2Shell: https://www.redtigersecurity.com/advisory/php2shell-cisa-kev-oct-2026 . https://www.redtigersecurity.com/advisory/php2shell-wago-festo-certvde
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources: CERT@VDE advisories, 10 November 2026: VDE-2026-128 https://certvde.com/en/advisories/VDE-2026-128/ ; VDE-2026-160 ; VDE-2026-141 ; VDE-2026-152 ; VDE-2026-131. All are listed at https://certvde.com/en/advisories/
Check out our resources and book a follow-up call with our team.