CERT@VDE, the industrial cybersecurity coordination center of the VDE Association for Electrical, Electronic and Information Technologies in Germany, has published two PHP2Shell advisories that put concrete patch and mitigation steps in the hands of plant owners. Advisory VDE-2026-132 covers multiple WAGO controllers and operator panels. Advisory VDE-2026-139 (external ID FSA-202603) covers Festo Didactic FactoryViews and MES4 training and manufacturing software. Both advisories are about the same two PHP flaws that the Cybersecurity and Infrastructure Security Agency (CISA) already listed in its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-109618, rated 9.8, and CVE-2026-109619, rated 8.1. PHP2Shell means a remote attacker can run their own code on a device or server that serves web pages with an affected copy of PHP, often with no login. This is the WAGO plant-controller and Festo Didactic training-stack wave that follows earlier PHP2Shell bulletins from Schneider Electric, ABB, B and R, Palo Alto Networks and others.
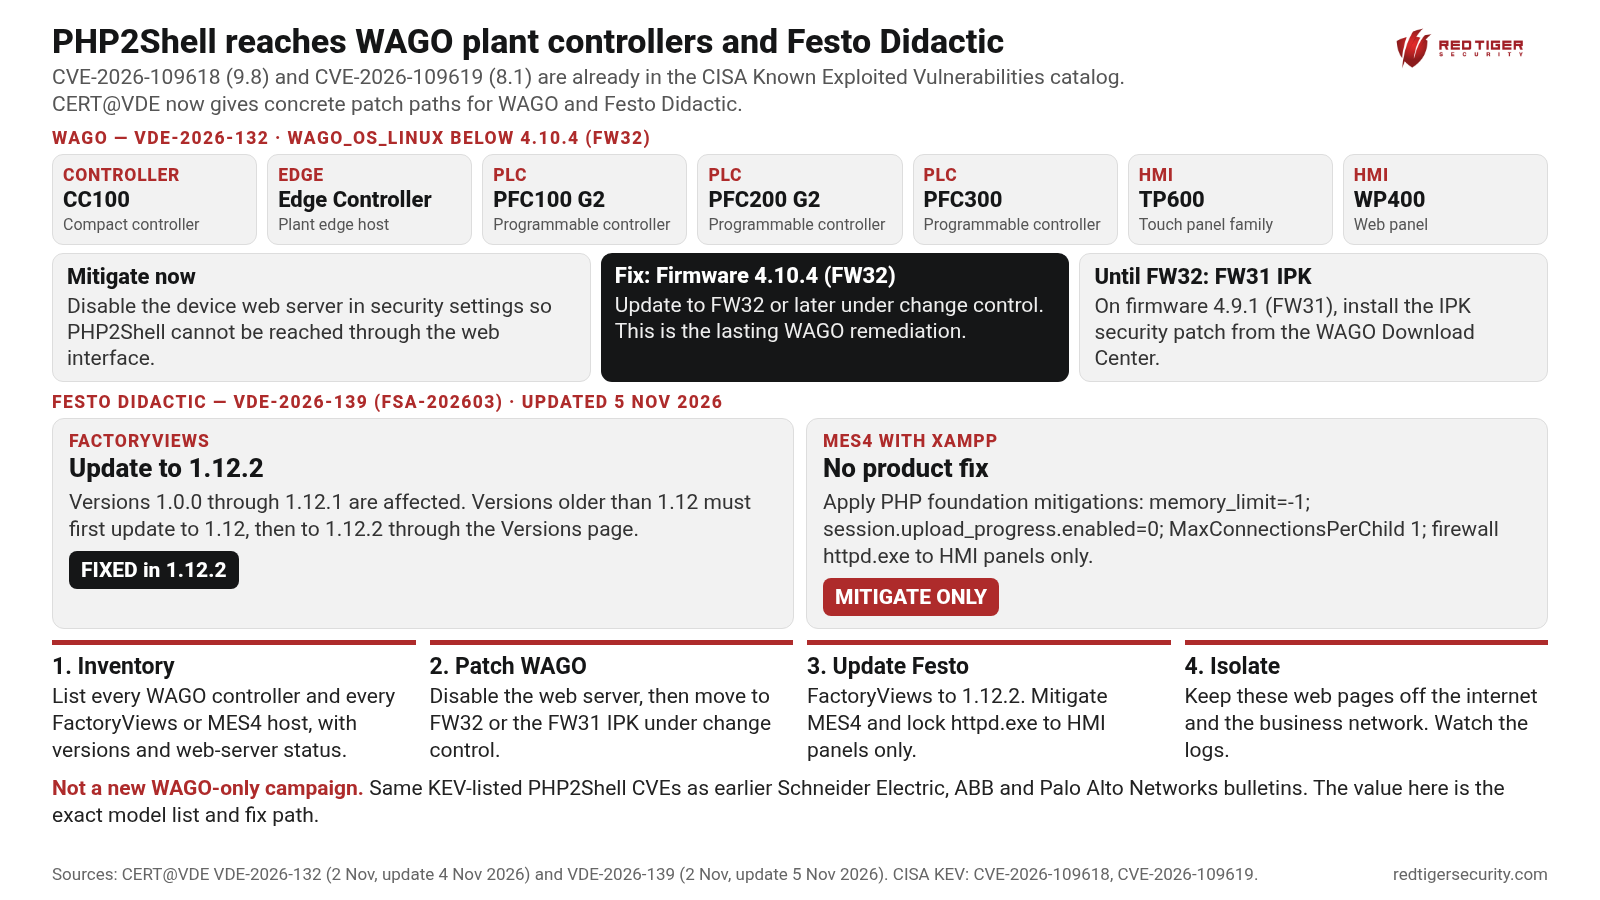
For WAGO (VDE-2026-132, published 2 November 2026 and last updated 4 November for a product-tree typo): devices running wago_os_linux below version 4.10.4, also called firmware FW32, are affected when the built-in web server is enabled. The listed products are the CC100 compact controller, the Edge Controller, PFC100 G2, PFC200 G2, PFC300, the TP600 touch panel family and the WP400 web panel. Until you can update, CERT@VDE says to disable the device web server through the security settings so the flaws cannot be reached through the web interface. The lasting fix is firmware 4.10.4 (FW32) or later. Until FW32 is available on a given controller, customers still on firmware 4.9.1 (FW31) should install the matching IPK security patch from the WAGO Download Center. An IPK is a small software package you install on the controller without replacing the whole firmware image.
For Festo Didactic (VDE-2026-139, published 2 November 2026 and last updated 5 November 2026 with adjusted vendor fix information): FactoryViews versions 1.0.0 through 1.12.1 and MES4 deployments that ship with XAMPP are affected. XAMPP is a bundled Apache web server and PHP stack that sits on the Windows host. Festo recommends updating FactoryViews to version 1.12.2 through the Versions page of the FactoryViews control panel. Versions older than 1.12 must first be updated to 1.12, then to 1.12.2. For MES4 with XAMPP there is no product fix. Apply the PHP foundation mitigations: set memory_limit=-1 in php.ini; set session.upload_progress.enabled=0 in php.ini; add MaxConnectionsPerChild 1 at the end of httpd-xampp.conf (this will slow the server); and use the Windows host firewall to keep httpd.exe reachable only from the human-machine interface (HMI) panels of the manual workstations, not from the rest of the plant or the internet.
WAGO programmable logic controllers (PLCs), edge controllers and touch panels are common in water, energy, chemical, packaging and building automation cabinets. Their web interfaces are often left on for commissioning and then forgotten. Festo Didactic FactoryViews and MES4 sit in training labs and on production lines that use Festo didactic stations, where a Windows PC with XAMPP becomes a quiet PHP host next to the HMI. CERT@VDE is not claiming a new WAGO-only or Festo-only attack campaign. The same two KEV-listed CVEs already have public proof-of-concept details, so the value of these bulletins is the exact model list, the FW32 and IPK path for WAGO, and the clear "update FactoryViews, mitigate MES4" split for Festo.
On the plant floor, affected WAGO controllers and panels sit inside cabinets and remote panels that talk to drives, input and output modules and operator stations. In the control room and Level 3 supervisory network, the same devices may present a web configuration page to engineering laptops. Festo FactoryViews and MES4 with XAMPP typically run on Windows hosts next to didactic or line HMIs, often on the same network segment as the training or production equipment. At the business edge, any of those web interfaces that can be reached from the office network or the internet is the first place an attacker tries PHP2Shell.
1. Inventory every WAGO CC100, Edge Controller, PFC100 G2, PFC200 G2, PFC300, TP600 and WP400 on site, plus every FactoryViews and MES4 with XAMPP host. Record the firmware or software version and whether the device web server is enabled.
2. On WAGO gear, disable the web server through security settings until you can move to firmware 4.10.4 (FW32) or later. If you are on FW31 (4.9.1) and FW32 is not yet available for that controller, install the IPK security patch from the WAGO Download Center under change control.
3. On Festo Didactic, update FactoryViews to 1.12.2 (step through 1.12 first if you are older than 1.12). For MES4 with XAMPP, apply the four PHP foundation mitigations above and firewall httpd.exe away from non-HMI sources. There is no MES4 product fix.
4. Keep these web interfaces off the internet and off the business network. Limit admin access to named engineering hosts, watch web server logs for odd requests, and treat any previously exposed host as a candidate for a deeper check.
Red Tiger Security has completed 500+ plant-safe operational technology (OT) assessments and trained 4,500+ engineers and operators. Our team can help you find which WAGO and Festo hosts are in scope, plan a plant-safe firmware and software update window, and set up 24x7 monitoring that flags unexpected web activity on controllers and training hosts.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
CERT@VDE VDE-2026-132, WAGO Multiple Devices affected by PHP2Shell, published 2 November 2026, last update 4 November 2026: https://certvde.com/en/advisories/VDE-2026-132
CERT@VDE VDE-2026-139, Two critical PHP vulnerabilities in several Festo Didactic products (FSA-202603), published 2 November 2026, last update 5 November 2026: https://certvde.com/en/advisories/VDE-2026-139
CISA Known Exploited Vulnerabilities catalog (CVE-2026-109618 and CVE-2026-109619): https://www.cisa.gov/known-exploited-vulnerabilities-catalog
Check out our resources and book a follow-up call with our team.