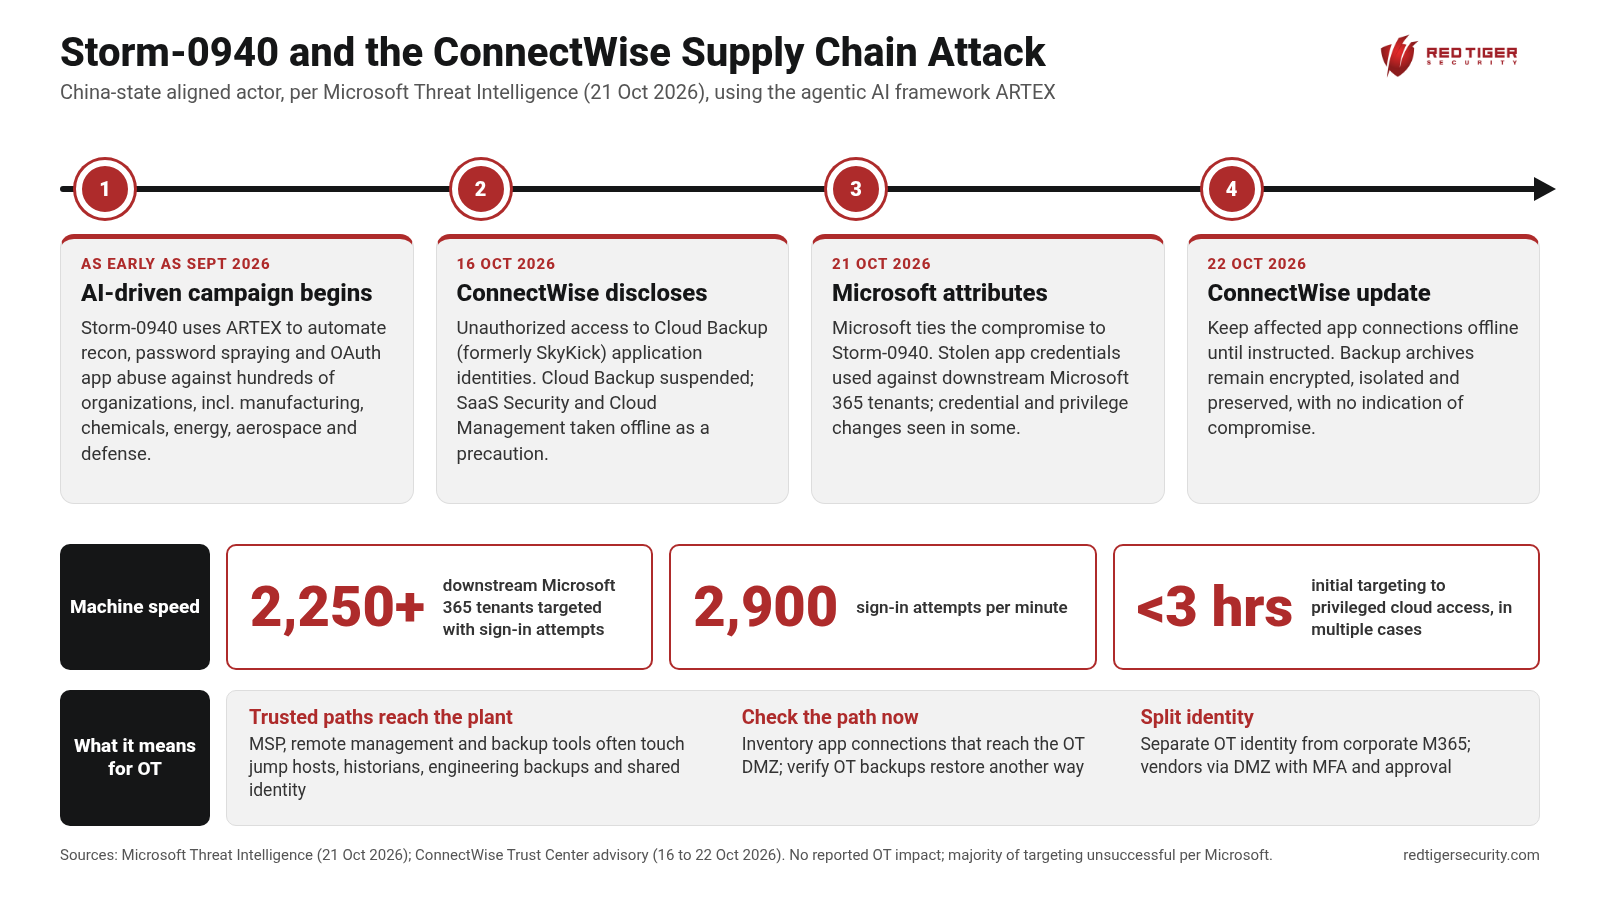
Microsoft Threat Intelligence published research on 21 October 2026 that ties a China-state aligned actor it tracks as Storm-0940 to the ConnectWise Cloud Backup (formerly SkyKick) supply chain compromise. ConnectWise has since said that, based on the evidence available to it, including threat intelligence shared by Microsoft, a China state-aligned group appears responsible.
Who the actor is:
• According to Microsoft, Storm-0940 has been active since 2021 and targets organizations across many industries for data theft. It has historically relied on password spraying and exploitation of internet-facing applications, and in cloud environments it has kept access by adding credentials to existing OAuth applications.
• Microsoft reports that, as early as September 2026, the actor began using ARTEX, an open-source agentic AI penetration testing framework, to automate reconnaissance and scanning, password spraying and OAuth application abuse.
What they target (high level):
• Hundreds of organizations worldwide. Microsoft lists aerospace and defense, automotive, chemicals, energy, financial services, government, manufacturing and semiconductors, among others.
• In the ConnectWise case, the target was trust that already existed: a backup application that MSPs and their customers had granted access to Microsoft 365 so it could back up and restore data.
What is new:
• Scale and speed. Microsoft says that, after the unauthorized access, Storm-0940 used ARTEX to attempt sign-ins to more than 2,250 downstream tenants at 2,900 sign-in attempts per minute. In multiple cases the time from initial targeting to privileged cloud access was under 3 hours.
• Microsoft says the majority of the targeting was not successful, but where it worked, it saw application credential changes and privilege changes that can stay in place as a backdoor after the original app is fixed. Microsoft also notes that an affected app or a successful sign-in does not by itself mean data was accessed, and that this was not a compromise of Microsoft systems.
• ConnectWise disclosed the incident on 16 October, suspended Cloud Backup and took SaaS Security and Cloud Management offline as a precaution. Its 22 October update says to keep affected application connections offline until it issues instructions, and that existing backup archives remain encrypted, isolated and preserved with no indication of compromise. It reports no indication that other ConnectWise products are affected.
What it means for OT owners:
Neither Microsoft nor ConnectWise reports any impact on OT systems. The lesson for water, electric, oil and gas, chemical, maritime and manufacturing operators is about the path. MSP tools, remote management and cloud backup sit on trusted connections into IT, and in many plants those same connections reach jump hosts, historians, engineering workstation backups and identity that is shared with the control network. Manufacturing, chemicals and energy were in the target set, and an AI-driven campaign that reaches privileged access in under 3 hours leaves very little time to notice and respond.
What the Red Tiger team recommends:
1. Inventory every third-party and MSP application connection and OAuth app with access to your Microsoft 365 tenant, and flag any that also reach the OT DMZ or plant systems.
2. Keep affected ConnectWise connections disabled until ConnectWise says otherwise, and confirm you can back up and restore through another path, including OT backups such as historian, HMI and controller project files.
3. Review application sign-ins, Microsoft Graph activity, new credentials and privilege changes from at least 15 October, and preserve logs before you change anything.
4. Separate OT identity and remote access from corporate Microsoft 365, and require vendor access through a controlled DMZ path with MFA and session approval.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: Microsoft Threat Intelligence: https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/
ConnectWise Trust Center advisory: https://www.connectwise.com/company/trust/advisories
Check out our resources and book a follow-up call with our team.
