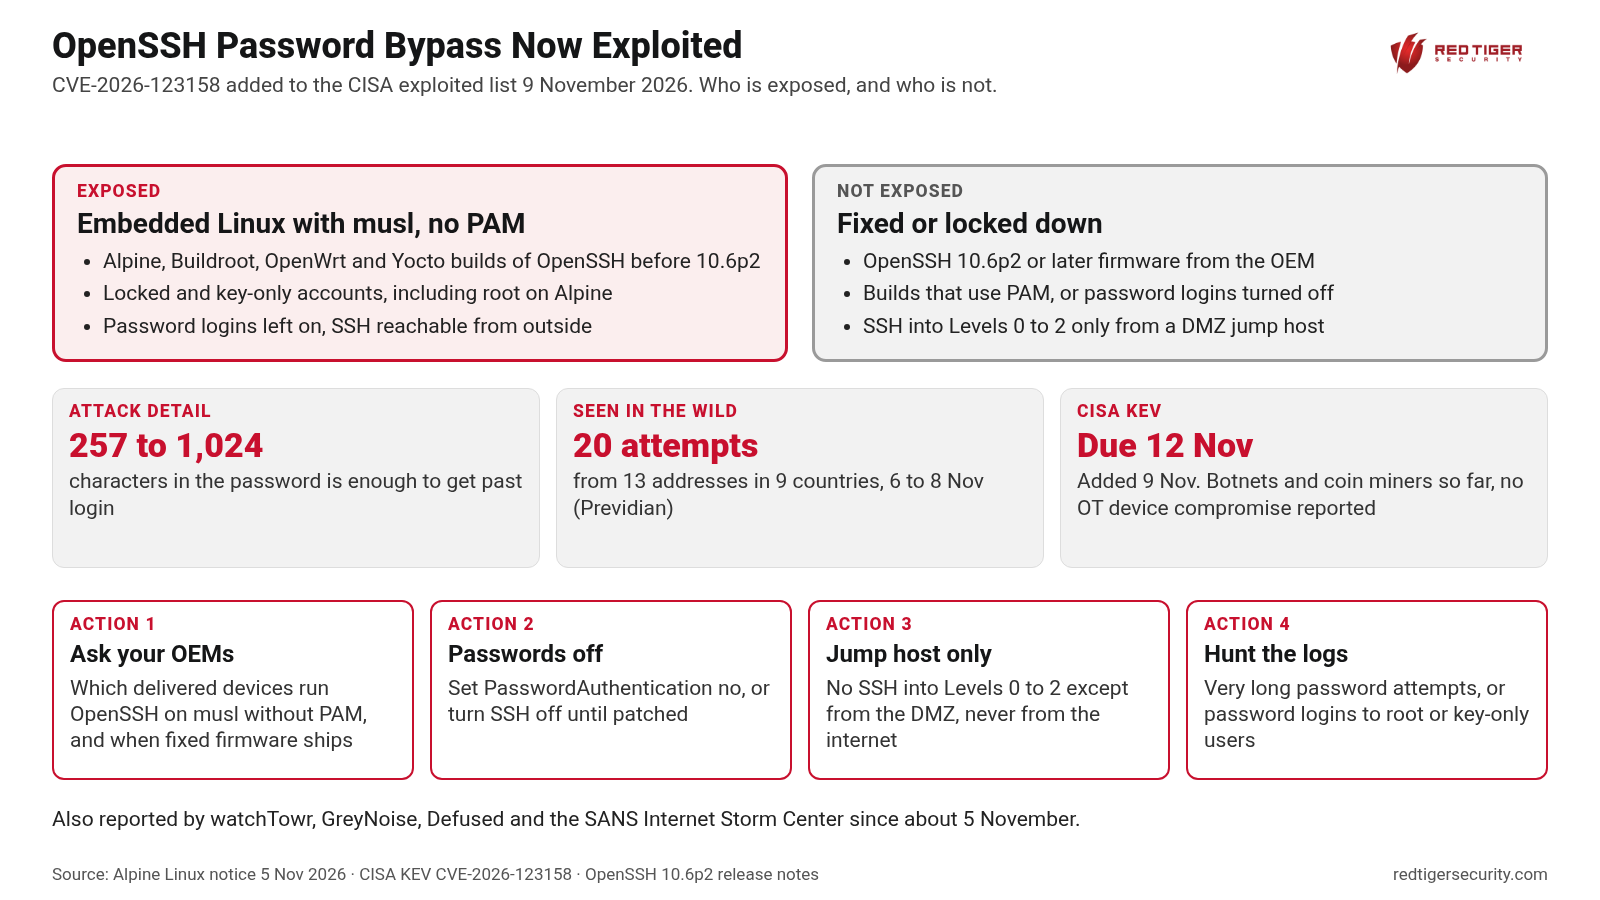
The OpenSSH password bypass the Red Tiger team warned about on 5 November is now being exploited. On 9 November the Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-123158 to its Known Exploited Vulnerabilities (KEV) catalog, with a federal fix deadline of 12 November.
The flaw only works on Linux builds of OpenSSH that use the musl C library and do not use Pluggable Authentication Modules (PAM). That sounds narrow, but it describes a lot of small embedded Linux: Alpine, Buildroot, OpenWrt and Yocto builds are the common ones. Those are the same build systems OEM vendors use for gateways, protocol converters, cellular routers, edge boxes and some human-machine interfaces (HMIs).
According to the Alpine Linux security notice, a password between 257 and 1,024 characters long can get past authentication for an account whose password field is set to a single asterisk. That is the normal setting for a locked account, which includes root on Alpine and any user who is meant to log in with a key only. In other words, the accounts that owners think are safest are the ones exposed. OpenSSH 10.6p2 fixes it.
Several honeypot and threat research teams have now seen the flaw used in the wild. watchTowr reported exploitation tied to botnets and cryptocurrency miners. Previdian logged 20 attempts from 13 internet addresses in nine countries between 6 and 8 November, including one that reached root on a decoy system. GreyNoise, Defused and the SANS Internet Storm Center have reported scanning and attempts since about 5 November. None of these reports describe a confirmed compromise of a production OT device so far. The activity is opportunistic, which is exactly how exposed field gateways get found.
Prior Red Tiger advisory: https://www.redtigersecurity.com/advisory/ssh-in-ot-oem-firmware
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources: Alpine Linux security notice (5 November 2026) https://alpinelinux.org/posts/2026-11-05-openssh-password-authentication-bypass/ ; CISA KEV entry CVE-2026-123158 (added 9 November 2026) https://www.cisa.gov/known-exploited-vulnerabilities-catalog ; OpenSSH release notes https://www.openssh.org/releasenotes.html ; SecurityWeek reporting on exploitation (9 November 2026).
Check out our resources and book a follow-up call with our team.