Siemens has confirmed active exploitation of CVE-2026-110936, a DLL side-loading flaw in Siemens Software Center, and CISA added it to the Known Exploited Vulnerabilities catalog yesterday. Software Center is the program Siemens customers use to download, install, activate and update the software they have bought. Every version before 4.0.9.8 is affected.
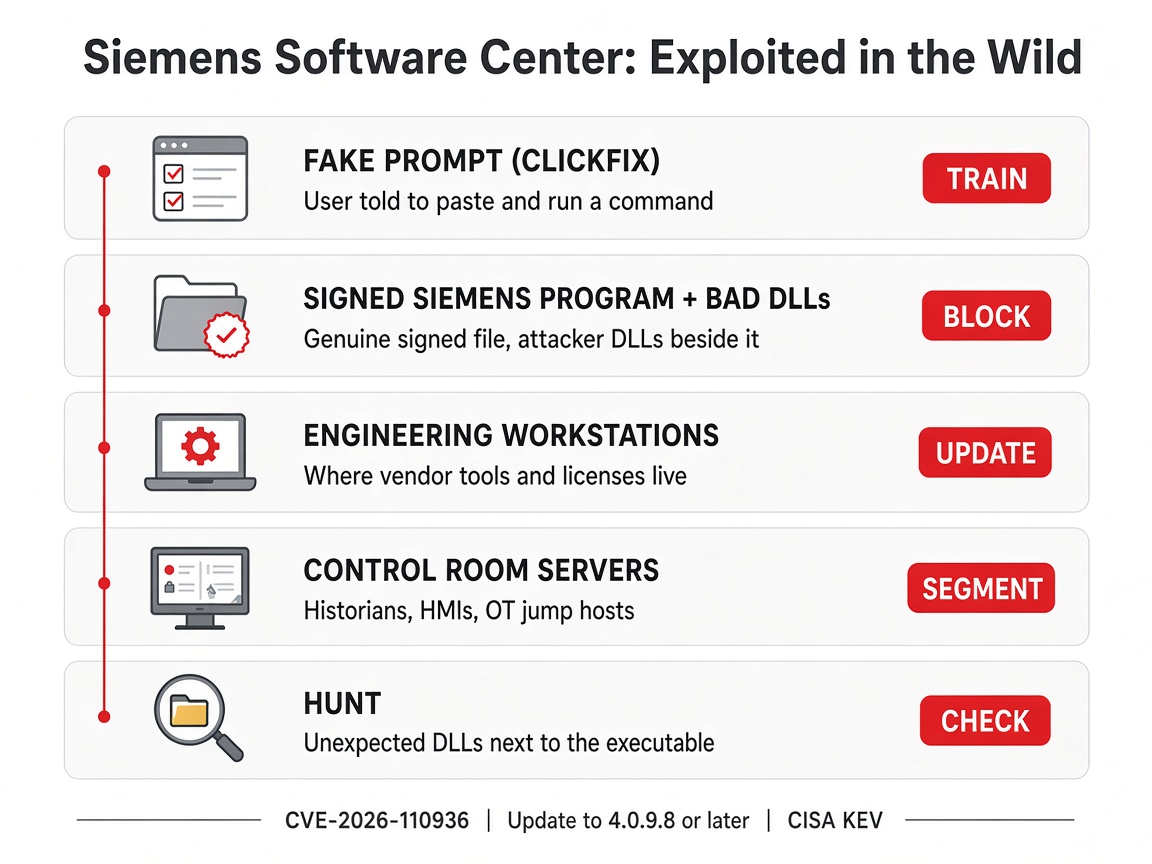
The attackers did not break into Siemens. Per Siemens, they took a genuine, digitally signed copy of Software Center and shipped it with their own malicious DLL files beside it, outside official Siemens channels. When the program starts, the vulnerable version loads those DLLs. Siemens tied the campaign to Romulus, a "ClickFix" operation that uses fake prompts, like bogus CAPTCHA checks, to get users to paste and run commands on their own machines.
Why this matters on the plant side:
- Engineering workstations. This is where vendor software, licenses and installers live, and where people go looking for downloads.
- Control room servers and jump hosts. A trusted, signed program running malicious code on a machine that can reach historians and HMIs is exactly what plant teams want to avoid.
- Enterprise and cloud. The lure starts in a web browser, so the business side and remote users are the front door.
What the Red Tiger team recommends this week:
- Update Siemens Software Center to 4.0.9.8 or later. Existing installs update automatically the next time they start, so open it and confirm the version.
- Get Siemens software only from official Siemens sources, and keep vendor installers off of OT machines unless they come through your change-control process.
- Block the indicators Siemens published on your firewalls, proxies and DNS, and search your logs for past connections.
- Look for Siemens Software Center running from unexpected folders, with extra DLL files sitting next to it. If you find it, isolate the machine and follow your incident response plan.
Cite this advisory: Red Tiger Security, "Siemens Software Center CVE-2026-110936 Exploited: What It Means for Engineering Workstations", October 21, 2026, https://www.redtigersecurity.com/advisory/siemens-software-center-cve-2026-110936