CISA pushed 17 Siemens ICS advisories out on 22 October. One of them, Siemens Software Center (CVE-2026-110936), is already on the Known Exploited Vulnerabilities list and we covered it earlier this week. The rest are not reported as exploited, but several sit right on the plant floor and a few have no fix yet.
The ones the Red Tiger team would look at first:
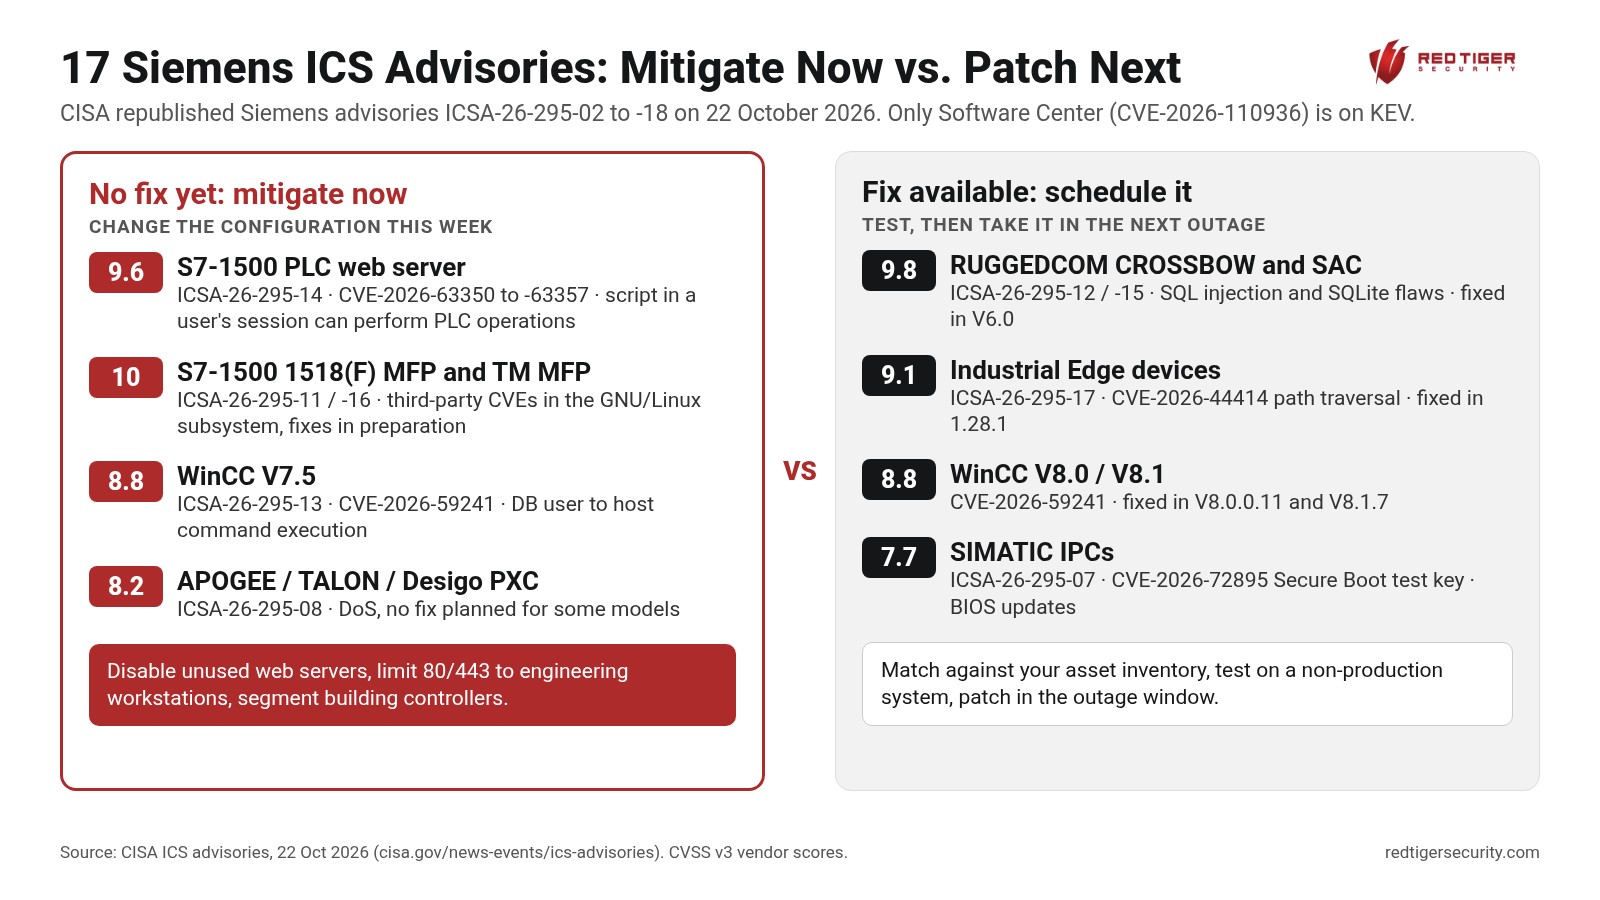
• SIMATIC S7-1500 PLC web server (ICSA-26-295-14, CVSS 9.6, CVE-2026-63350 through CVE-2026-63357): flaws that let an attacker run script in an authorized user's browser session and perform PLC operations within that user's rights. No fix is available yet. Siemens says to disable the web server where it is not needed, restrict ports 80/443 to trusted addresses, and only upload trusted trace files.
• SIMATIC S7-1500 CPU 1518(F)-4 PN/DP MFP and S7-1500 TM MFP (ICSA-26-295-11 and -16, CVSS 10): hundreds of third-party CVEs in the additional GNU/Linux subsystem. Siemens is preparing fixes and lists mitigations.
• RUGGEDCOM CROSSBOW and CROSSBOW Station Access Controller (ICSA-26-295-12 and -15, CVSS 8.8 and 9.8): SQL injection, credential exposure and SQLite flaws in the remote access management system many utilities use for substation and field devices. Fixed in V6.0.
• SIMATIC WinCC (ICSA-26-295-13, CVE-2026-59241, CVSS 8.8): an authenticated database user can execute commands on the host. Fixed in V8.0.0.11 and V8.1.7; V7.5 has no fix yet.
• APOGEE, TALON and Desigo PXC/PXM building controllers (ICSA-26-295-08, CVSS 8.2): denial of service flaws, with no fix planned for some models. Segmentation is the answer there.
• Also in the batch: SIMATIC IPC Secure Boot bypass through a test key (CVE-2026-72895), Industrial Edge devices and App Publisher, RUGGEDCOM APE1808, PSS SINCAL, SENTRON 3NA COM Fuse and the S7 Webserver API .NET client library.
Where this shows up from the plant floor to the cloud: S7-1500 controllers and MFP modules at Levels 1 and 2, WinCC SCADA servers and engineering stations at Levels 2 and 3, SIMATIC IPCs and Industrial Edge devices bridging Level 3 to the cloud, CROSSBOW on the remote access path into substations and field sites, and APOGEE/Desigo in building systems that often share the network with process control.
What the Red Tiger team recommends now:
1. Pull your asset inventory and match it against these 17 advisories. Most Siemens sites will have at least one S7-1500 or WinCC node on the list.
2. Turn off the S7-1500 web server where nobody uses it, and lock 80/443 down to engineering workstations where they do. Do this now, since there is no fix yet.
3. Schedule the patches you can take (CROSSBOW V6.0, WinCC V8.0.0.11/V8.1.7, SIMATIC IPC BIOS updates, Industrial Edge 1.28.1) into your next outage window, tested on a non-production system first.
4. Keep building automation controllers and remote access servers in their own zones, and watch for unexpected PLC changes and web server logins.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: https://www.cisa.gov/news-events/ics-advisories/icsa-26-295-14
CISA ICS advisories: https://www.cisa.gov/news-events/cybersecurity-advisories/ics-advisories
Check out our resources and book a follow-up call with our team.
