Two days after the PHP project patched the two "PHP2Shell" flaws (CVE-2026-109618 and CVE-2026-109619), industrial vendors are confirming that the bug reaches into OT products. Schneider Electric published security bulletin SESB-2026-295-01 on 22 October, and ABB published two advisories on 23 October, one for its Manufacturing Execution System (MES) and one for the B&R APROL process control system. Both CVEs allow unauthenticated remote code execution on servers running affected PHP versions. ABB rates them at CVSS 3.1 9.8 and 8.1, and 9.2 each under CVSS 4.0.
What the vendors say so far:
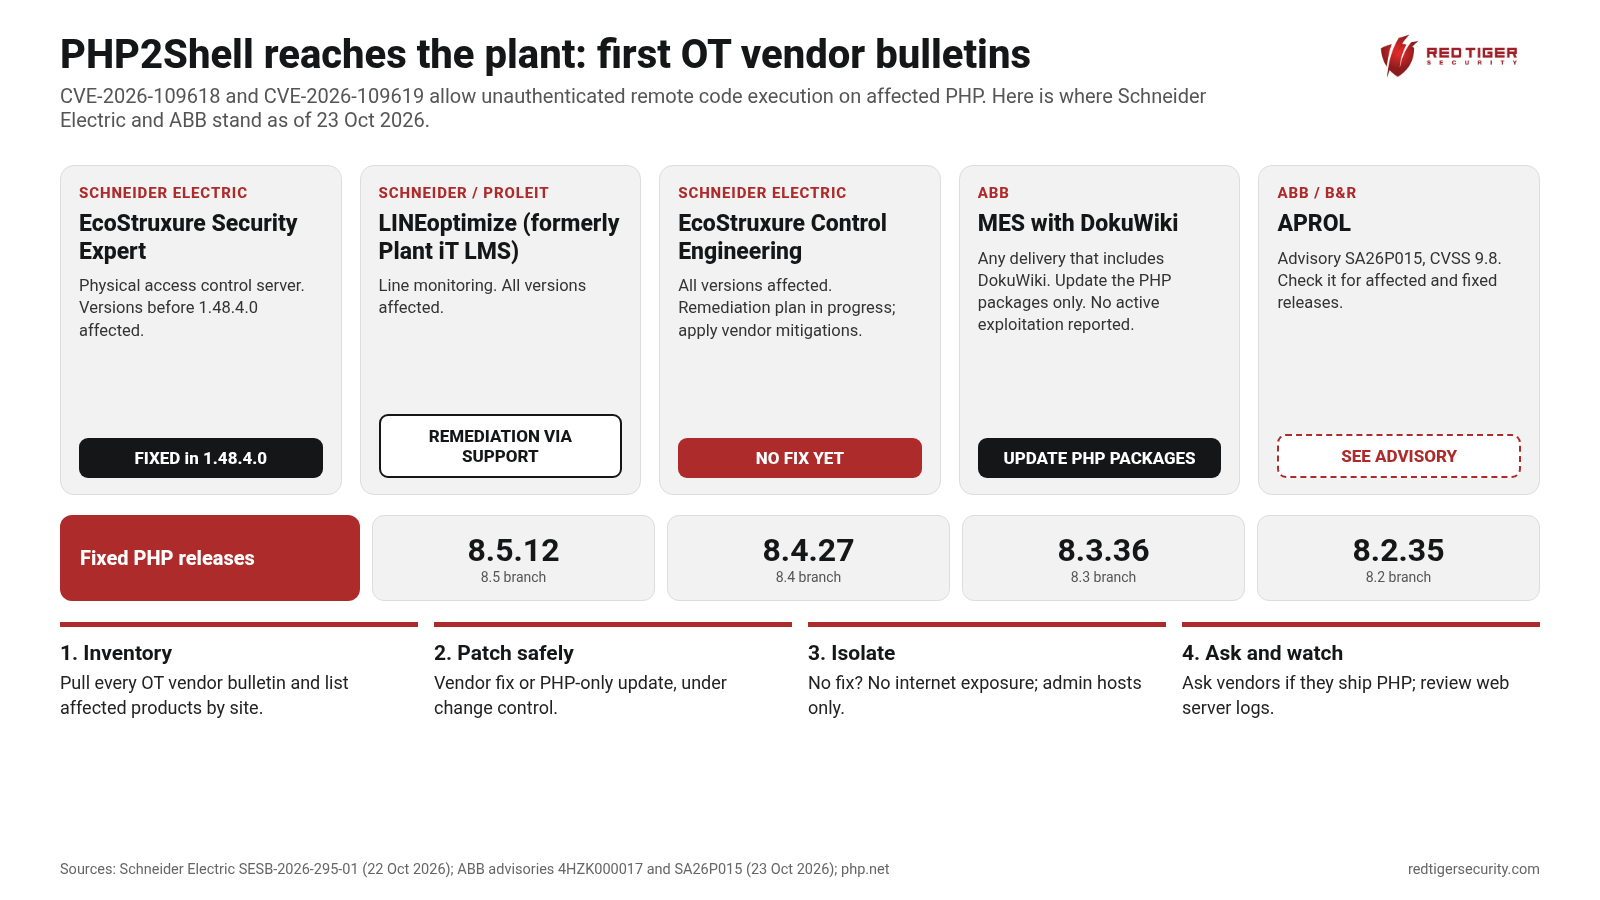
- Schneider Electric EcoStruxure Security Expert: all versions before 1.48.4.0 are affected; 1.48.4.0 includes the fix and is available through Schneider's Customer Care Center.
- ProLeiT LINEoptimize (formerly Plant iT LMS): all versions affected; a remediation is available through ProLeiT support.
- Schneider Electric EcoStruxure Control Engineering: all versions affected; no product fix yet, and Schneider says it is establishing a remediation plan and points customers to its mitigations.
- ABB MES: any delivery that includes DokuWiki is affected. ABB says to update only the PHP packages on the server to 8.5.12, 8.4.27, 8.3.36 or 8.2.35, not the whole DokuWiki installation, and reports no active exploitation at the time of writing.
- B&R APROL: ABB lists a 9.8 advisory, "APROL Impact of PHP2Shell" (SA26P015); check the advisory for affected and fixed releases.
Why this matters for OT owners: this is the pattern we flagged when PHP2Shell first came out. PHP rarely shows up on an asset list by name. It rides inside a vendor product: an access control server, a line monitoring system, an MES wiki, an engineering tool, a process control system's web services. The plant team often does not own the operating system underneath, so the PHP package does not get patched with the rest of IT. Canada's Cyber Centre reports that a proof of concept is public, with no active exploitation identified yet, so the window to get ahead of this is now. Expect more vendor bulletins over the next few weeks.
Where it shows up, plant floor to cloud: field devices and controllers rarely run PHP, but the Level 3 servers around them do. MES and production wikis, line and energy monitoring, and engineering and historian web portals sit in the control network or the Level 3.5 DMZ. Physical access control servers often bridge security and corporate networks. Any of those that serve a web page to untrusted users is a path in.
What the Red Tiger team recommends:
1. Pull the bulletins for every OT vendor you run (Schneider, ABB and B&R so far) and build a short list of affected products at each site. Ask your other vendors and integrators in writing whether their products ship PHP.
2. Patch in vendor-approved order. Use the vendor's fixed release where one exists, or update only the PHP packages where the vendor says to (as ABB does for MES). Follow change control on live OT and test before rolling out.
3. Where there is no fix yet, such as EcoStruxure Control Engineering, take the web interface off any network it does not need, keep it behind a firewall with no internet exposure, and restrict access to named admin hosts.
4. Watch the web servers. Review web server and application logs and look for unexpected processes, new files or outbound connections from PHP or web-server services on these hosts.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources: Schneider Electric SESB-2026-295-01: https://download.se.com/files?p_Doc_Ref=SESB-2026-295-01&p_File_Name=SESB-2026-295-01.pdf&p_enDocType=Security+and+Safety+Notice
ABB cyber security advisories (MES 4HZK000017, APROL SA26P015): https://www.abb.com/global/en/company/about/cybersecurity/alerts-and-notifications
Canadian Centre for Cyber Security AL26-026: https://www.cyber.gc.ca/en/alerts-advisories/al26-026-critical-vulnerabilities-impacting-php-cve-2026-109618-cve-2026-109619
Check out our resources and book a follow-up call with our team.
