CISA put out an alert today asking organizations to patch two critical PHP vulnerabilities right away, CVE-2026-109618 and CVE-2026-109619, also called "php2shell." They allow unauthenticated remote code execution on any PHP installation that serves web requests. The fixed versions are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
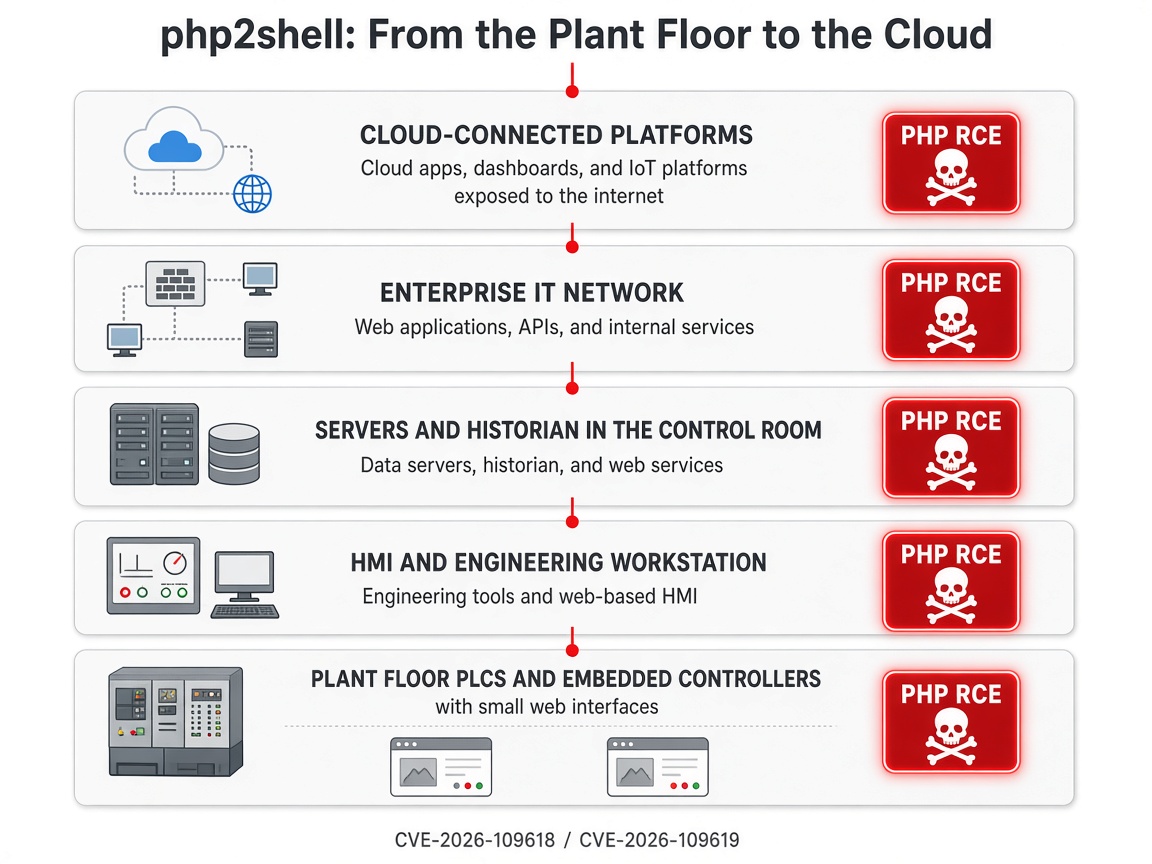
For industrial operators, the hard part is finding where PHP actually runs. It is often buried inside other products, and it shows up at every level of the plant:
- Field devices and embedded controllers. Many PLCs, RTUs, gateways, protocol converters and network switches ship with a small built-in web server for setup and diagnostics. Some of those run PHP, and nothing on the faceplate tells you so.
- HMIs and engineering workstations. Web-based HMIs and vendor configuration tools often run a local web stack.
- Control room servers. Historians, alarm management, reporting portals and asset inventory tools often have a PHP web front end.
- Enterprise and cloud-connected systems. Remote access portals, IoT and analytics platforms, ticketing and monitoring dashboards, and the vendor cloud services that pull plant data upward. These usually face the internet, which makes them the first place an attacker will look and the first place to patch.
A compromised web service at any of these levels can become a foothold that leads down toward the control network. What the Red Tiger team recommends this week:
- Inventory anything that serves web pages, from the perimeter down to the field, and ask your OEMs and integrators directly whether their products include PHP.
- Patch internet-facing systems first. For OT devices, follow the vendor's firmware guidance and your change-control process, and do not patch live controllers blind.
- Systems that can't be patched yet, or that run PHP 8.1 or older, should be taken offline or isolated behind a firewall or a web application firewall.
- Watch for web or PHP worker processes that launch shells or download tools, and for any new outbound connections from those systems.
CISA has not seen exploitation yet, so there is still a window to get ahead of this. If you need help finding PHP in your OT environment or isolating systems you can't patch yet, the Red Tiger team can help.
CISA alert: https://www.cisa.gov/news-events/alerts/2026/10/21/critical-vulnerabilities-php-require-immediate-patching
Cite this advisory: Red Tiger Security, "php2shell: Critical PHP Vulnerabilities, From the Plant Floor to the Cloud", October 21, 2026, https://www.redtigersecurity.com/advisory/php2shell-critical-php-vulnerabilities