Nozomi Networks Labs published "OT/IoT Fields Hot Summer Cyber Trends of 2026" on 12 October, a look at anonymized customer telemetry and honeypot data from June through August 2026. The headline is not a new zero-day or a clever new actor. It is that most of what hit OT and IoT environments this summer came in through the same old doors.
What the data shows (per Nozomi Networks Labs):
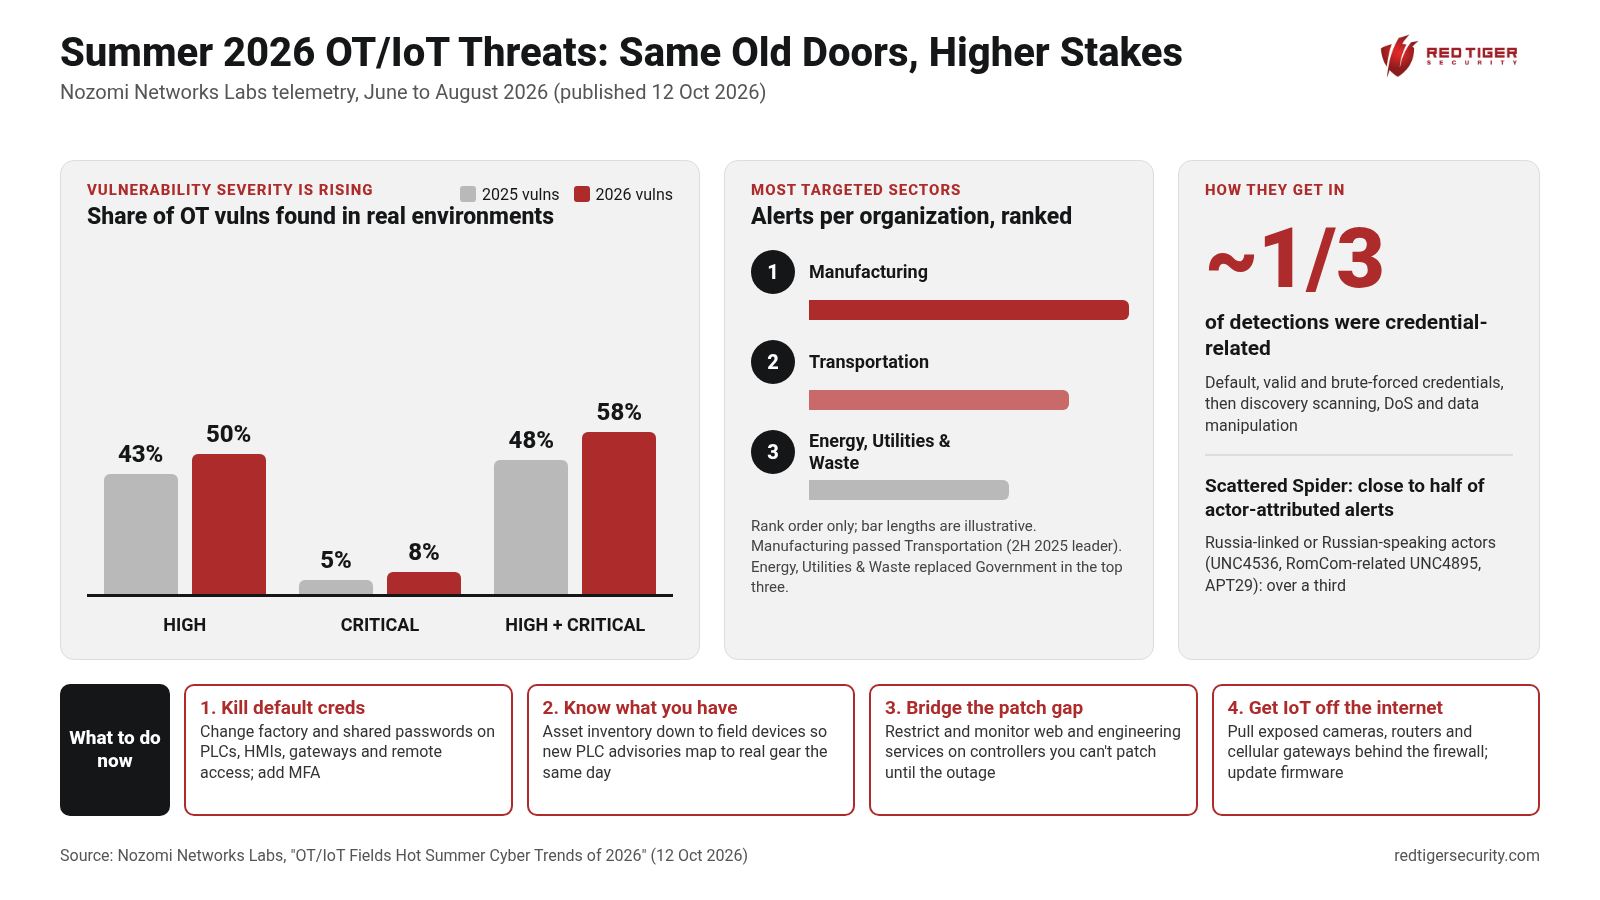
• Credential-related techniques (default, valid and brute-forced credentials) accounted for roughly a third of all observed detections. Discovery scanning, Denial of Service and Data Manipulation round out the common pattern.
• Manufacturing took first place for alerts per organization, ahead of Transportation. Energy, Utilities and Waste moved into third, replacing Government.
• Scattered Spider was tied to close to half of all actor-attributed alerts. Russia-linked or Russian-speaking actors (UNC4536, the RomCom-related UNC4895 and APT29) together accounted for over a third.
• Of the 2026 OT vulnerabilities found in real environments, 50% were rated HIGH and 8% CRITICAL, up from 43% and 5% for 2025 vulnerabilities. The most frequently detected ones affect widely deployed PLCs, including Siemens and Rockwell Automation.
• Botnets kept growing. Nozomi's honeypots recorded attacks from 1,716 unique IP addresses on 29 August, the busiest day, and new IoT botnet families (Apex2, c2c/meow, Tengu, Kataru, and the Golang-based Kairos) were observed.
What is new:
The severity mix is shifting. HIGH and CRITICAL combined rose from 48% to 58% year over year, and Nozomi notes that AI is shortening the window between disclosure and exploitation. Energy, Utilities and Waste climbing into the top three also lines up with the attacks on water and power this year.
Where this shows up, plant floor to cloud:
• Field and Level 1: PLCs, IO-Link masters and fieldbus gateways that sit right next to the process and are hard to patch on short notice.
• Control network: engineering workstations, HMIs and historians reachable with shared or default accounts.
• Perimeter and remote access: VPNs, jump hosts and vendor connections where valid credentials are the way in.
• IoT and cloud edge: cameras, routers and cellular gateways recruited into botnets because they are exposed and still on factory passwords.
What it means for OT owners:
None of the top techniques need a zero-day. A default password on a gateway, a shared engineering account, or a camera sitting on the internet gives an attacker the same foothold. At the same time, the share of serious PLC vulnerabilities is climbing on assets that can only be patched during planned outages, so compensating controls have to carry the load in between.
What the Red Tiger team recommends:
1. Kill default and shared credentials. Inventory accounts on PLCs, HMIs, gateways and remote access, change factory passwords, and put MFA on every path into the control network.
2. Know what you have. Build a current asset inventory down to the field devices, so a new HIGH or CRITICAL PLC advisory can be matched to real assets the same day.
3. Bridge the patch gap. For controllers you cannot patch until the next outage, restrict access to their web and engineering services, segment them, and monitor for Discovery, DoS and unauthorized writes.
4. Get IoT off the internet. Find exposed cameras, routers and cellular gateways, pull them behind the firewall or VPN, update firmware and watch for unusual outbound traffic.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: Nozomi Networks Labs, OT/IoT Fields Hot Summer Cyber Trends of 2026 (12 Oct 2026): https://www.nozominetworks.com/blog/ot-iot-fields-hot-summer-cyber-trends-of-2026
Check out our resources and book a follow-up call with our team.
