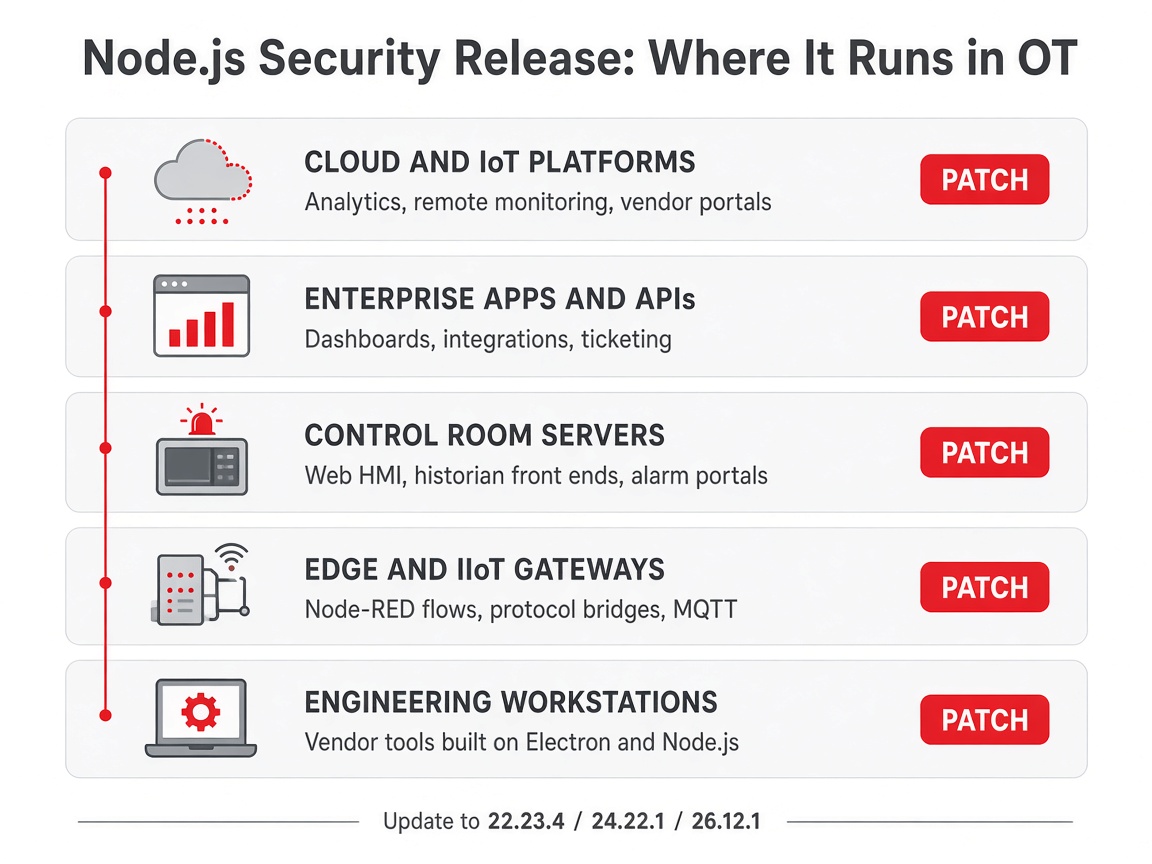
The Node.js project pushed out security releases today for all three supported lines: 22.23.4, 24.22.1 and 26.12.1. The update fixes ten vulnerabilities, four of them rated high. The most serious is CVE-2026-111497, an out-of-bounds write in the Brotli decompression code that can allow remote code execution. Two other high-rated flaws, CVE-2026-105483 and CVE-2026-106069, let a TLS certificate hostname check be bypassed. The fourth, CVE-2026-105482, truncates DNS names that contain a NUL character.
Most people think of Node.js as a web developer's tool, but it shows up all over industrial environments:
- Edge and IIoT gateways. Node-RED flows, protocol bridges and MQTT brokers that move data from the field up to the historian or the cloud.
- Control room servers. Web HMIs, historian front ends and alarm portals built on Node.js.
- Engineering workstations. Many vendor configuration and programming tools are Electron apps with Node.js inside, and they don't get patched through Windows Update.
- Enterprise and cloud-connected systems. Remote monitoring, analytics and vendor portals, where the TLS flaws matter most because certificate checks are what keep those plant-to-cloud connections trusted.
What the Red Tiger team recommends this week:
- Find where Node.js runs, including inside vendor products and Electron apps, and ask your OEMs and integrators which of their releases include it.
- Update internet-facing and cloud-connected systems first, then gateways and servers, using your normal change-control process on live OT.
- Anything on Node.js 20.x or older is end of life and stays exposed. Plan to replace it, and isolate it until you do.
- Watch Node.js processes for unexpected child processes, outbound connections or certificate errors.
CISA has not issued an alert, and no exploitation has been reported. That is the time to get ahead of it.
Node.js advisory: https://nodejs.org/en/blog/vulnerability/october-2026-security-releases
Cite this advisory: Red Tiger Security, "Node.js October 2026 Security Release: Where It Runs in OT", October 21, 2026, https://www.redtigersecurity.com/advisory/nodejs-october-2026-security-release