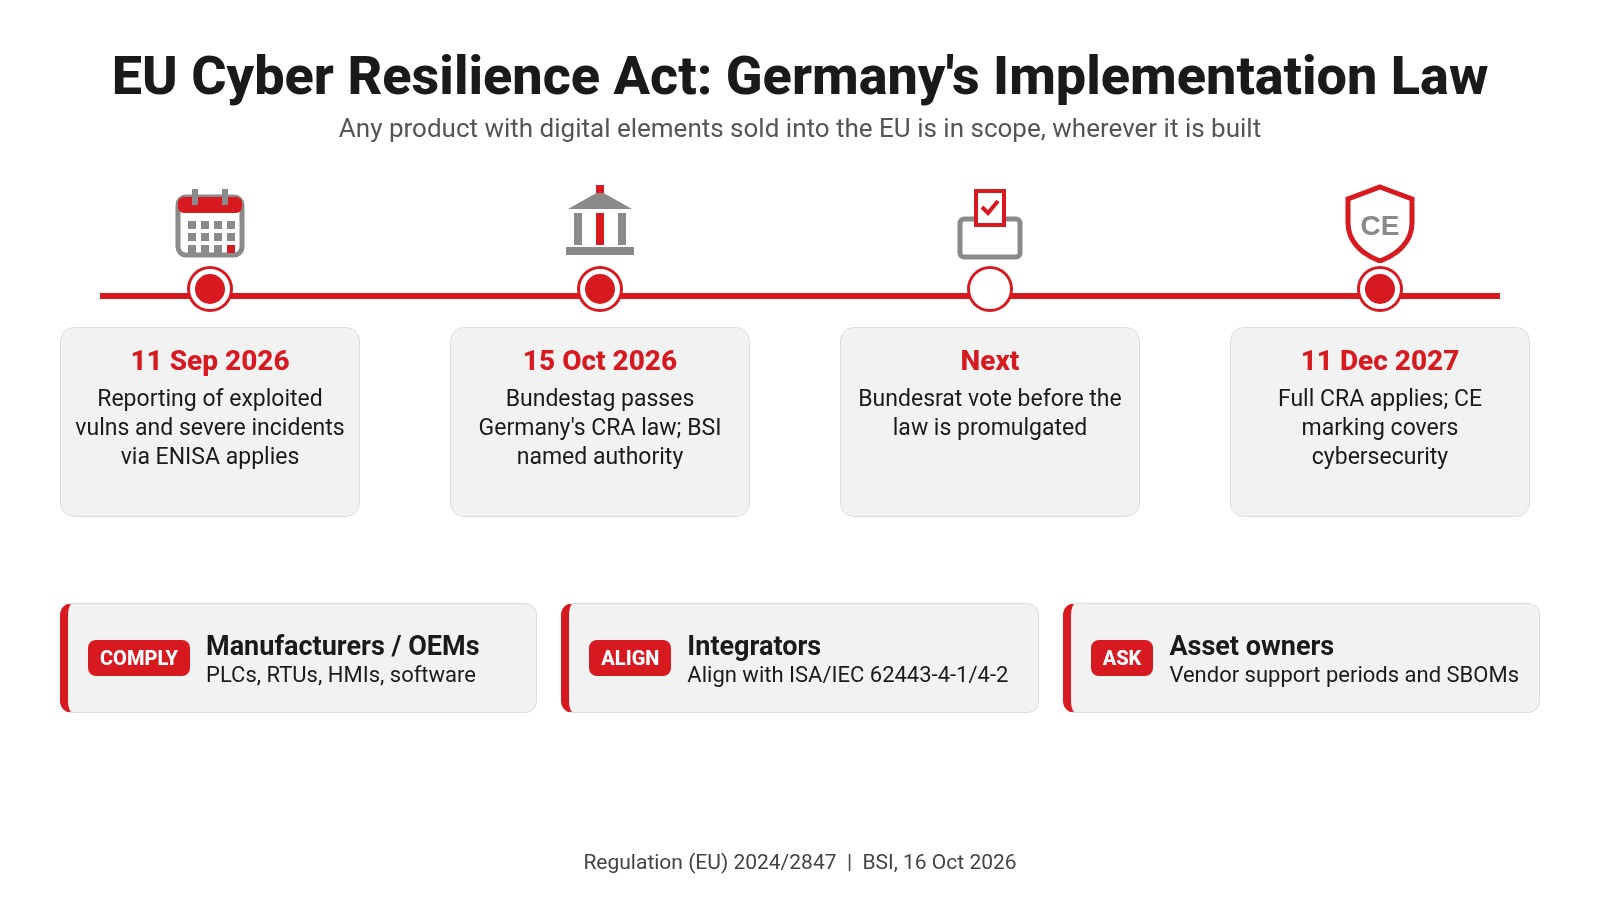
Germany's Bundestag passed the national law that puts the EU Cyber Resilience Act (CRA) into force in Germany on 15 October. It names the BSI, Germany's federal cyber agency, as the authority that checks products on the market and approves the bodies that assess them. The bill still needs Bundesrat approval before it is promulgated, and Italy is working through a similar decree that names its agency, ACN.
Why this matters outside of Europe: the CRA applies to any product with digital elements sold into the EU, no matter where it was built. Per the BSI, the authority will be able to test products, demand fixes, issue fines and pull products off the market. CE marking will cover cybersecurity starting in December 2027.
Who it touches, from the plant floor to the cloud:
- Manufacturers and product vendors. PLCs, RTUs, HMIs, gateways, firmware, engineering software and cloud-connected devices sold in the EU.
- Integrators. The panels, skids and systems you ship into Europe are built on those products.
- Asset owners. Your vendors' support periods, patch process and documentation will change, and that affects your lifecycle planning in the US as well.
The dates to plan around (Regulation (EU) 2024/2847):
- 11 September 2026: reporting of actively exploited vulnerabilities and severe incidents already applies. The BSI has coordinated CRA reports for Germany since that day.
- 11 December 2027: the full CRA applies, including the product security requirements.
What the Red Tiger team recommends now:
- Vendors: list which of your products are sold into the EU and confirm you can report an exploited vulnerability through ENISA's reporting platform today.
- Vendors and integrators: line up your secure development and patch processes against ISA/IEC 62443-4-1 and 4-2, the basis for the CRA standards still in progress.
- Asset owners: ask your OT vendors for their CRA support period, SBOM and vulnerability disclosure plans, and add those questions to new purchase specs.
- Everyone: track the Bundesrat vote and the other member state laws, since each country will enforce through its own authority.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
BSI (German): https://www.bsi.bund.de/DE/Service-Navi/Presse/Pressemitteilungen/Presse2026/261020_CRA-Durchf%C3%BChrungsgesetz.html
Cite this advisory: Red Tiger Security, "Germany Passes Its EU Cyber Resilience Act Law: What OT Vendors and Asset Owners Should Do Now", October 21, 2026, https://www.redtigersecurity.com/advisory/cra-germany-implementation-law