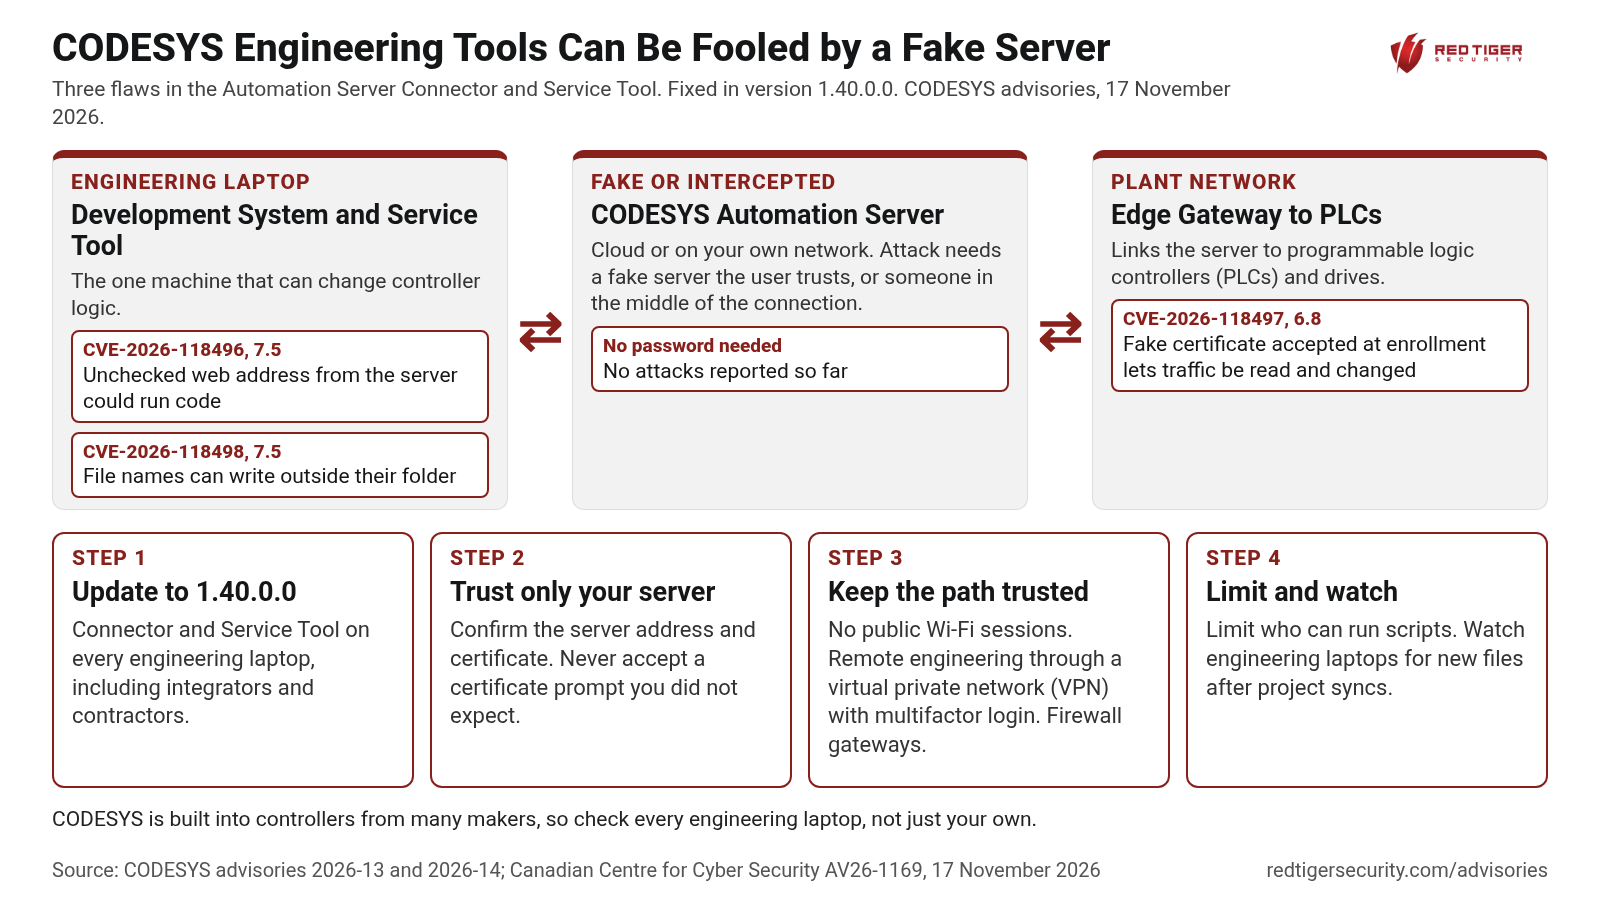
CODESYS GmbH published two security advisories on 17 November 2026 covering three vulnerabilities in the CODESYS Automation Server Connector and the CODESYS Service Tool, and the Canadian Centre for Cyber Security repeated the warning the same day in its advisory AV26-1169. CODESYS is the programming software that many controller and drive makers build into their products, so it sits on a lot of engineering laptops in plants. The Automation Server Connector is an add-on for the CODESYS Development System that syncs projects with the CODESYS Automation Server, the company's central project and device management platform, and configures CODESYS Edge Gateways, the small services that link that server to the controllers on the plant network. The Service Tool is a separate program for setting up those Edge Gateways. CODESYS has fixed all three flaws in version 1.40.0.0 of both products. None of the sources report attacks in the wild.
All three need the user's machine to talk to a server that is fake or being intercepted, and none of them needs a password. That is why the attack has a high complexity rating, but it is also why the engineering workstation is the target.
Red Tiger's view is that the real exposure here is the engineering laptop. It is the one machine that can change the logic in your controllers, and it often travels between sites, the office network, hotel Wi-Fi and vendor networks. When that laptop reaches out to an Automation Server, whether it is hosted in the cloud or on a server in your own network, the tools covered by these advisories decide whether to trust what comes back. If that trust can be faked, an attacker who gets on the same network path, such as a shared contractor network or a poorly segmented plant network, can turn the engineering tool against the plant.
On the plant side, Edge Gateways connect the Automation Server to the programmable logic controllers (PLCs) and drives. CVE-2026-118497 matters there because a bad certificate accepted during enrollment can let someone watch and change traffic between the server and the controller network. Integrators and machine builders who use the Automation Server to manage customer projects should treat this as their own patch as well, because their laptops visit many plants.
Red Tiger can help with this beyond the assessment itself. During our onsite facility assessments, our team inventories engineering workstations and the software they run, reviews how they reach controllers and remote servers, and works with operators and integrators on a patching plan that keeps the plant running. We can also install a firewall and sensor at the site, connect them to the Red Tiger 24x7 security operations center (SOC), and monitor the plant for ongoing detection and response, with regular metrics and reports. Our team has completed more than 500 assessments and trained more than 4,500 people.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: Canadian Centre for Cyber Security, CODESYS security advisory AV26-1169, 17 November 2026: https://www.cyber.gc.ca/en/alerts-advisories/control-systems-codesys-security-advisory-av26-1169
Check out our resources and book a follow-up call with our team.