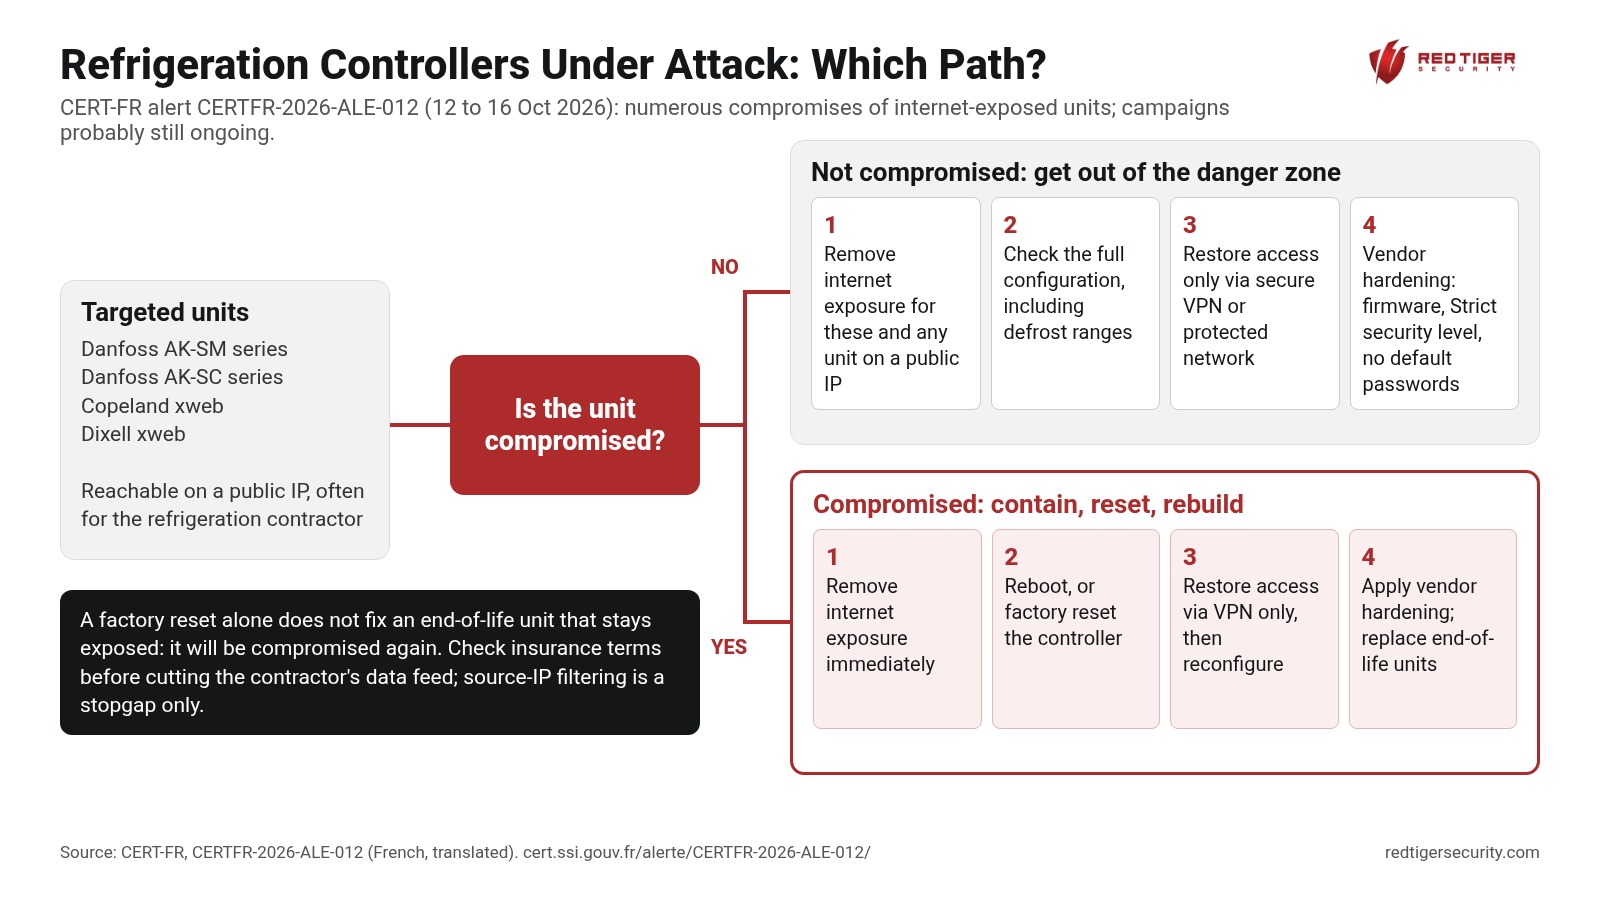
France's national CERT (CERT-FR) is warning about an active campaign against internet-exposed refrigeration remote controllers. Alert CERTFR-2026-ALE-012, first issued 12 October and updated 13 and 16 October, says CERT-FR is aware of numerous compromises of Danfoss AK-SM and AK-SC series controllers and Copeland and Dixell xweb supervisors. CERT-FR adds that attack campaigns against this equipment are probably still ongoing.
Why this matters to OT owners: these controllers run cold storage, food and beverage processing, pharmaceutical and chemical storage, grocery distribution and the cold rooms that sit inside plants, terminals and ports. They are often installed and remotely managed by a refrigeration contractor, so they tend to sit outside the OT asset inventory and outside the firewall rules the plant team owns. CERT-FR specifically tells owners to check the whole configuration after an incident, including defrost schedules, which is a reminder that a "facilities" device can still change a physical process and spoil product.
Where it shows up, plant floor to cloud:
• Field level: compressors, evaporators, case and cold room sensors wired to the controller.
• Control level: the Danfoss AK-SM/AK-SC or xweb supervisor that sets setpoints, alarms and defrost cycles.
• Remote access: a public IP, port forward or cellular modem so the refrigeration contractor can log in and pull data.
• Cloud and vendor side: contractor monitoring portals and data uploads that insurance contracts may require.
What CERT-FR recommends (translated from the French alert):
• If the equipment is not compromised: remove internet exposure for these units and any other unit on a public IP, check the full configuration including defrost ranges, restore access only through a secure VPN or protected network, and apply the vendor's hardening guidance (for Danfoss: update firmware, set security level to Strict, change default passwords).
• If the equipment is compromised: remove internet exposure, reboot or factory reset the controller, restore access only through a VPN or protected network, reconfigure it, then apply the vendor hardening guidance.
• CERT-FR warns that a factory reset alone is not enough for end-of-life units that cannot be patched. They will be compromised again if they stay exposed.
• Check insurance contract terms before cutting the contractor's internet data feed. Filtering the contractor's source IPs on a firewall is acceptable as a stopgap only, not a lasting fix.
What the Red Tiger team recommends now:
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: CERT-FR alert CERTFR-2026-ALE-012 (French): https://www.cert.ssi.gouv.fr/alerte/CERTFR-2026-ALE-012/
Check out our resources and book a follow-up call with our team.
