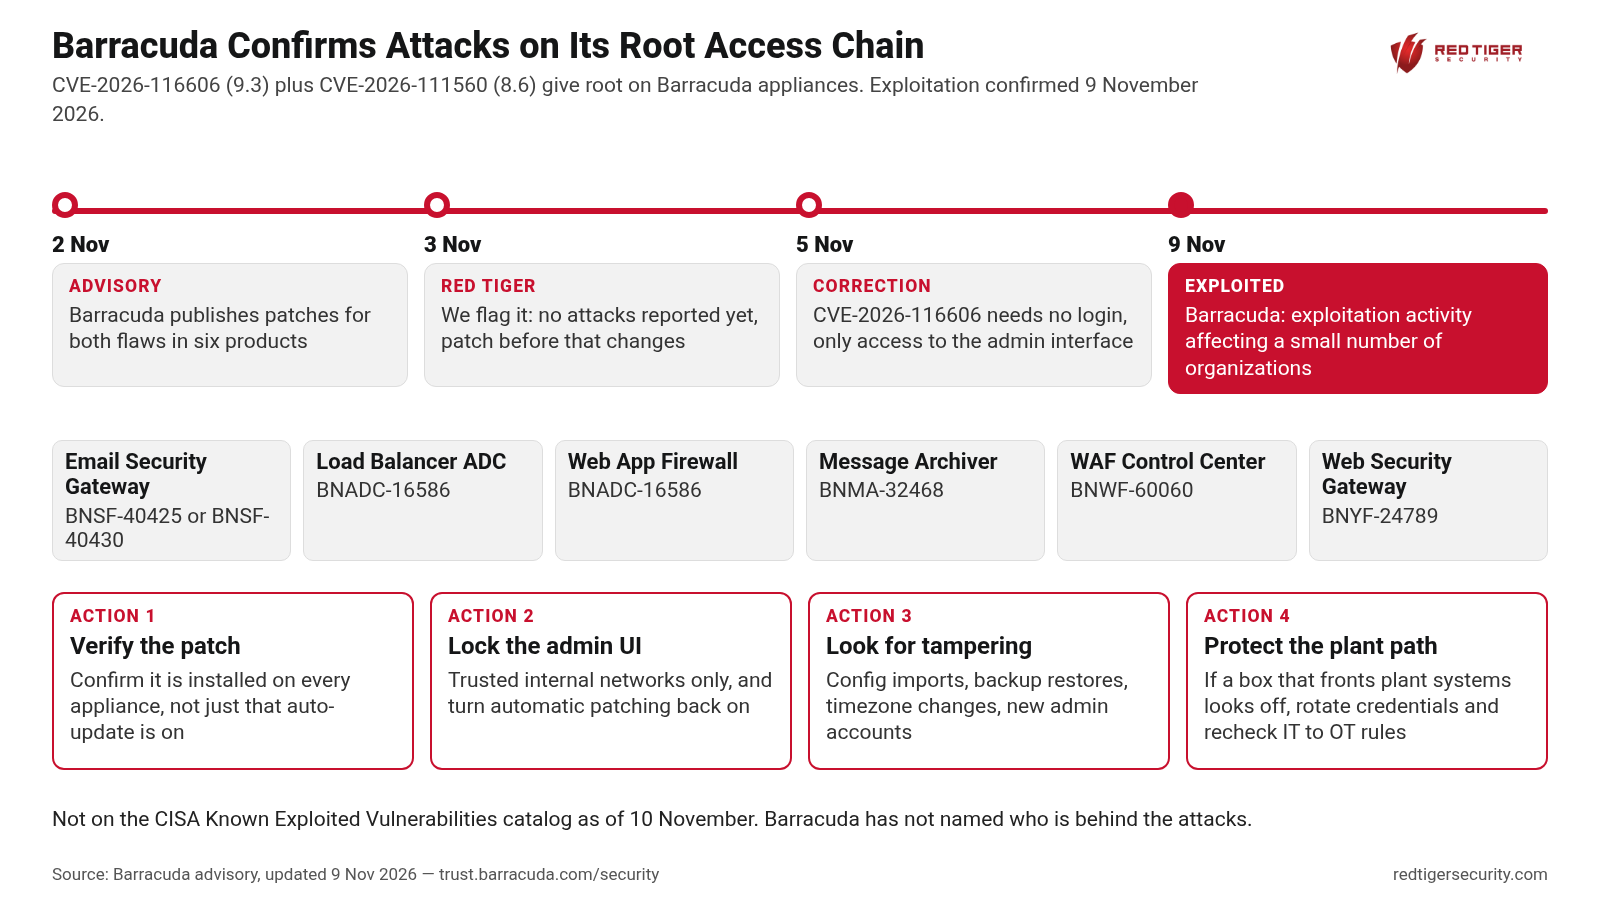
Barracuda Networks now says attackers are using the two flaws the Red Tiger team flagged on 3 November. In an update to its advisory posted the evening of 9 November 2026, Barracuda wrote that it has identified exploitation activity affecting a small number of organizations. When we first reported these flaws, Barracuda had not reported any attacks, and neither flaw is on the Known Exploited Vulnerabilities (KEV) catalog of the Cybersecurity and Infrastructure Security Agency (CISA) as of this advisory.
Barracuda published the advisory on 2 November. On 5 November it corrected the login requirement for CVE-2026-116606 from administrative access to no authentication required, as long as the attacker can reach the administrative user interface. On 9 November it added the exploitation note. The flaws themselves have not changed:
CVE-2026-116606 is an authorization bypass in the Email Security Gateway (ESG), rated 9.3 on the Common Vulnerability Scoring System (CVSS). CVE-2026-111560 is a command injection flaw in the timezone setting, rated 8.6, and it affects six products: the Email Security Gateway, the Load Balancer Application Delivery Controller (ADC), the Message Archiver, the Web Application Firewall (WAF), the WAF Control Center and the Web Security Gateway. Chained together, the two give an attacker root access to the appliance.
These boxes are usually run by IT, but they sit on the paths into many industrial companies. The email gateway handles the mail that reaches engineers and operators. Web application firewalls and load balancers often front vendor portals, historian web views and remote access pages. An attacker with root on one of those appliances can read traffic, harvest credentials and move toward the plant network.
Prior Red Tiger advisory: https://www.redtigersecurity.com/advisory/barracuda-esg-waf-root-chain
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: Barracuda advisory, updated 9 November 2026 https://trust.barracuda.com/security/pre-authentication-authorization-bypass-command-injection
Check out our resources and book a follow-up call with our team.