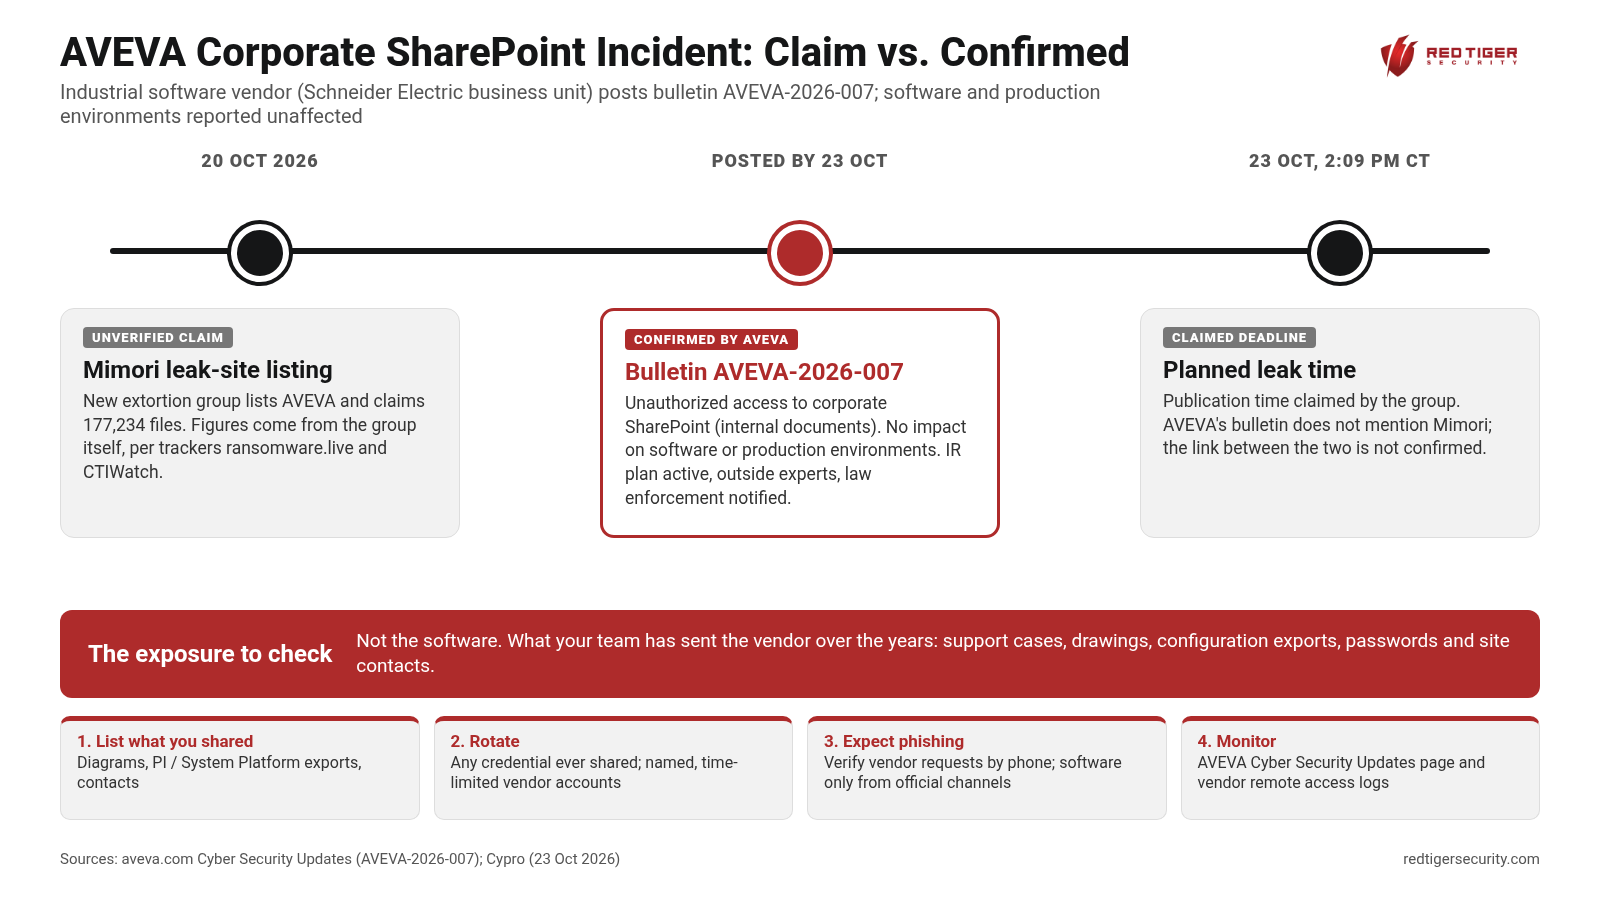
AVEVA, the industrial software company and Schneider Electric business unit behind PI System, System Platform, InTouch, Plant SCADA and Enterprise SCADA, has posted security bulletin AVEVA-2026-007 on its Cyber Security Updates page. The company says it is investigating unauthorized access to its corporate SharePoint, an internal document repository. AVEVA says that, as things stand, there is no impact on its software or production environments, which are separate. It has activated its incident response plan, brought in outside cybersecurity experts and notified law enforcement, and says it will issue further notifications if the investigation finds material impact on third parties.
The bulletin follows a claim posted on 20 October 2026 by a new extortion group calling itself Mimori, which listed AVEVA on its leak site and claimed 177,234 files, with a planned publication time of 23 October (19:09 UTC, 2:09 PM CT), according to leak-site trackers ransomware.live and CTIWatch as reported by Cypro. AVEVA's bulletin does not mention Mimori, and the file count and leak date come from the group itself. Neither has been independently verified.
Why this matters for OT owners: AVEVA software runs in control rooms across oil and gas, power, water, chemicals and manufacturing. A corporate document repository at any major OT vendor can hold support cases, project files, architecture drawings, site contacts and configuration exports shared by customers and integrators. AVEVA says no specific defensive measures are needed for its products, and nothing here points to a vulnerability in AVEVA software. The exposure to think about is whatever your own team has shared with the vendor.
What the Red Tiger team recommends:
1. Make a quick list of what your team has sent to AVEVA (or any OT vendor) through support cases, shared folders and email: network diagrams, PI or System Platform configuration exports, credentials, site contact lists.
2. Rotate any credential, service account or remote access secret that has ever been shared with a vendor, and move vendor access to named, time-limited accounts.
3. Expect follow-on phishing that uses real project or support details. Tell engineers and procurement to verify unexpected vendor requests, invoices or "urgent patch" files by phone with a known contact, and only install software from AVEVA's official channels.
4. Watch AVEVA's Cyber Security Updates page and your account team for further notices, and review your remote access logs for vendor accounts.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources: AVEVA Security Bulletin AVEVA-2026-007: https://www.aveva.com/en/support-and-success/cyber-security-updates/
Cypro (23 Oct 2026), Mimori claim unconfirmed: https://cypro.co.uk/insights/cyber-bulletins/aveva-ransomware-claim-by-mimori-unconfirmed/
Check out our resources and book a follow-up call with our team.
