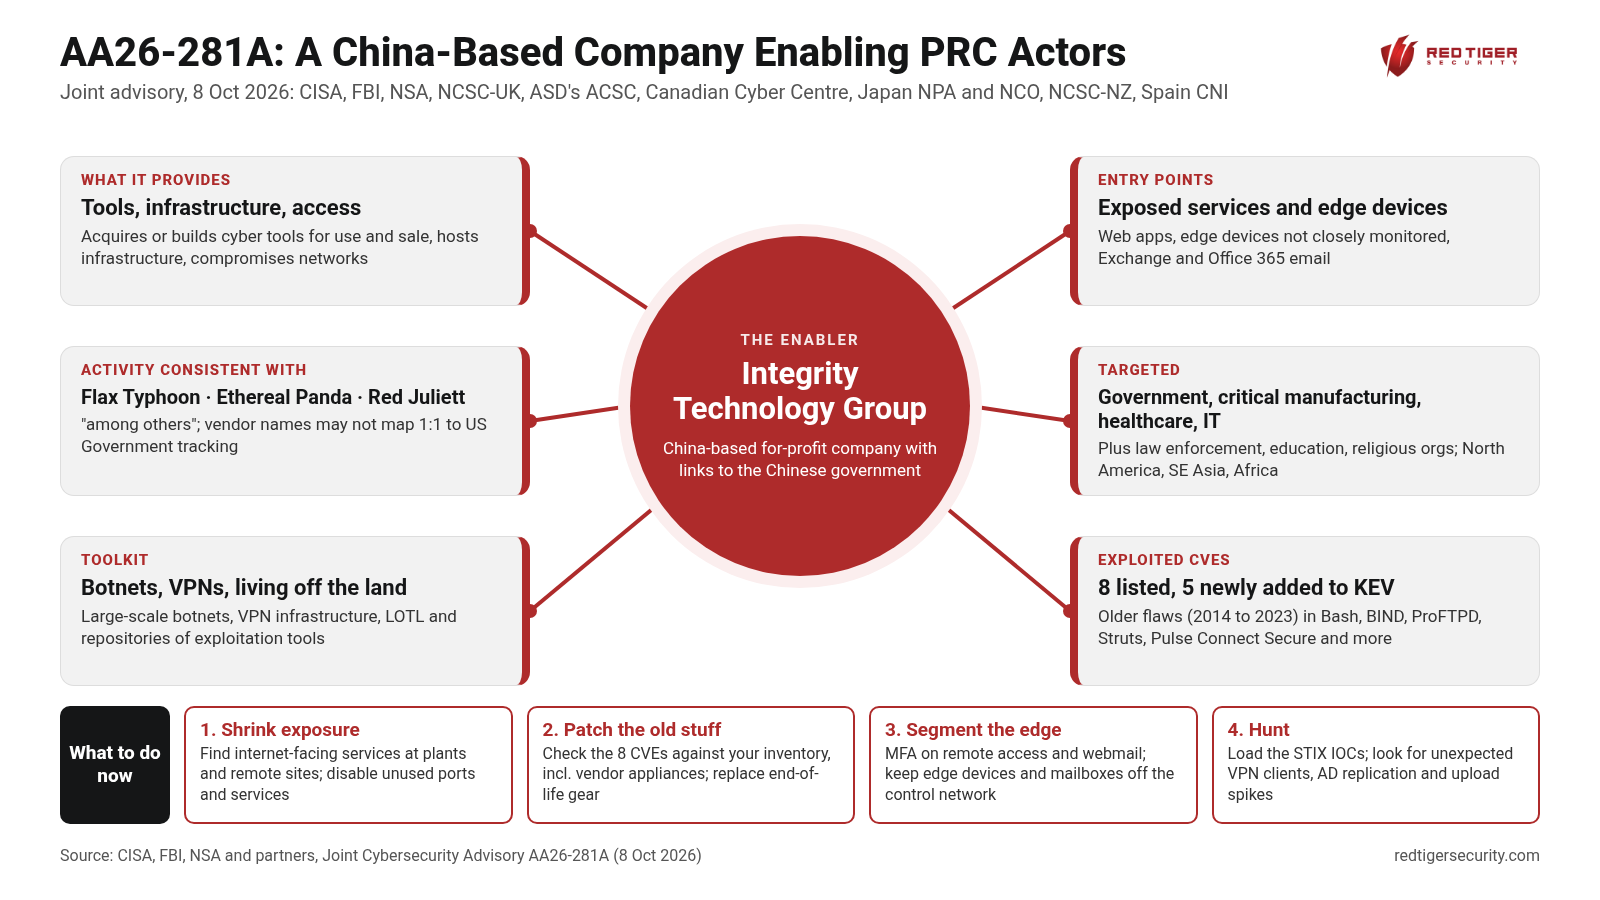
CISA, the FBI and NSA, with partners in the UK, Australia, Canada, Japan, New Zealand and Spain, released joint Cybersecurity Advisory AA26-281A on 8 October 2026. This one names a company, not just a hacking group: Integrity Technology Group (Integrity Tech), a China-based for-profit cybersecurity company the agencies say has links to the Chinese government.
Who they are:
- According to the authoring agencies, Integrity Tech employs people who acquire or build cyber tools for use and sale, acquire and host infrastructure, and compromise networks around the world.
- The actors it enables use tactics consistent with activity publicly known as Flax Typhoon, Ethereal Panda and Red Juliett, among others. The agencies note that vendor tracking names may not match the US Government's view 1:1, and that these actors may also run activity not tied to Integrity Tech.
What they target (high level):
- US Government Services and Facilities, Critical Manufacturing, Healthcare and Public Health, and Information Technology, plus law enforcement, education and religious organizations. Activity was also observed in North America, Southeast Asia and Africa.
- Exposed web applications and services, Microsoft Exchange and Office 365 email, Active Directory credentials, and, per CISA, edge devices that are not closely monitored by the targeted organization.
What is new:
- The advisory is based on evidence from multiple FBI investigations into Integrity Tech, and it treats the company as the enabler alongside the actors. The FBI says it pursues both the actors and the enterprises that support them.
- It describes a combination of large-scale botnets, VPN infrastructure, living-off-the-land techniques and repositories of exploitation tools, including a web scanning platform with more than 1,300 scripts in use since as early as 2017, and a legitimate VPN client installed on victim systems so the traffic blends in.
- It lists eight successfully exploited CVEs, five of them newly added to CISA's KEV catalog. Most are years old (2014 to 2023). IOCs are published in STIX format.
What it means for OT owners:
Most of the named sectors are IT-facing, but CISA's Acting Executive Assistant Director for Cybersecurity, Chris Butera, said Chinese government-affiliated actors continue to position themselves within critical infrastructure networks, including OT systems, with the aim of disrupting critical functions at a future time of their choosing. For water, electric, oil and gas, chemical, maritime and manufacturing operators, the entry points in this advisory are the ones that sit just above the plant: remote access VPNs and firewalls nobody reviews, older web servers and appliances that never got patched, and corporate email and Active Directory accounts that also open a path toward the control network.
What the Red Tiger team recommends:
- Shrink exposure. Find every internet-facing service at your plants and remote sites, disable unused services and ports, and require MFA on remote access and webmail.
- Patch the old stuff. Check the advisory's CVE list (Bash, BIND, ProFTPD, Apache Struts, Pulse Connect Secure, GitLab, ONLYOFFICE, Strapi) against your inventory, including vendor appliances, and replace end-of-life products.
- Segment the edge. Keep IT and OT separated so a compromised edge device or mailbox cannot reach the control network, segment edge devices internally, and review perimeter firewall rules for unauthorized changes.
- Hunt. Load the STIX IOCs and look for unexpected VPN clients, unexpected Active Directory replication, abnormal logons, and unusual upload volumes from hosts that normally upload very little.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: CISA, FBI, NSA and international partners: https://www.cisa.gov/news-events/news/cisa-fbi-nsa-and-international-partners-warn-china-based-cybersecurity-company-enabling-threat
Full advisory AA26-281A: https://www.cisa.gov/news-events/cybersecurity-advisories/aa26-281a