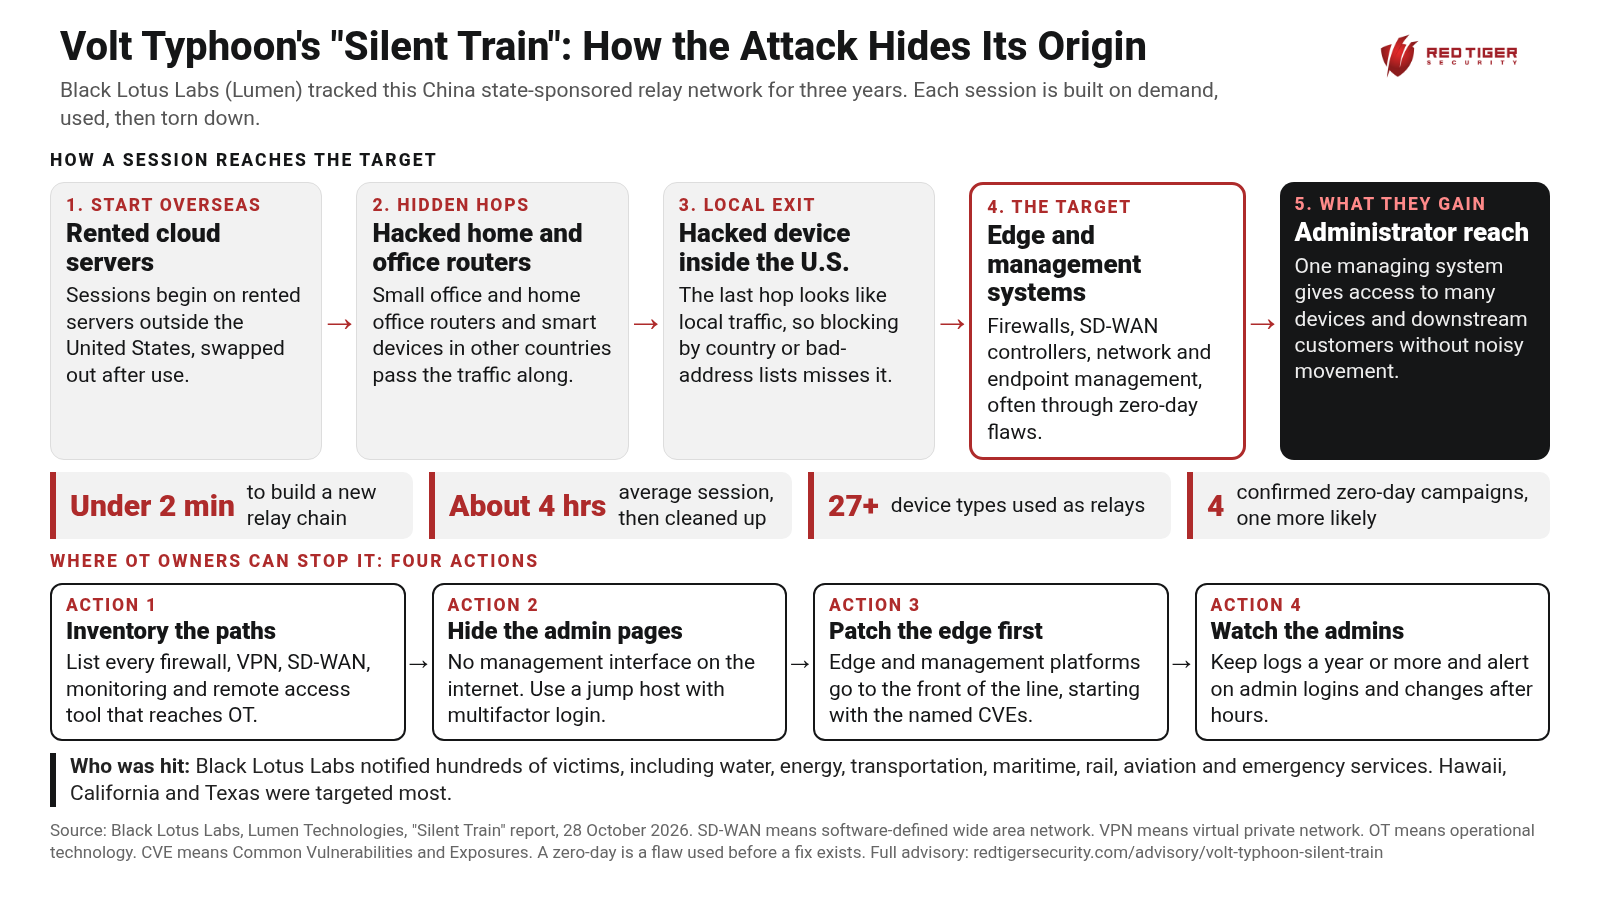
On 28 October 2026, Black Lotus Labs, the threat research team at Lumen Technologies, published a report on "Silent Train," a covert relay network used by Volt Typhoon, a hacking group sponsored by the People's Republic of China (PRC). Black Lotus Labs says it has tracked Silent Train for three years, notified hundreds of victims and helped uncover at least four confirmed zero-day campaigns, plus one likely campaign. A zero-day is a flaw that attackers use before the vendor knows about it or has a fix. According to the report, victims included critical infrastructure in the water, energy, transportation, maritime, rail, aviation and emergency services sectors.
Who the actor is. Volt Typhoon is the PRC state-sponsored group that United States officials publicly warned about in January 2024. According to Nextgov, officials assessed that it was targeting systems like power grids and transportation networks to be able to sabotage them if the United States became involved in a conflict over Taiwan. The Federal Bureau of Investigation (FBI) disrupted Volt Typhoon's earlier router network, the KV-botnet, starting in December 2023. Black Lotus Labs says it first saw consistent Silent Train activity in November 2023, and that activity increased after the KV-botnet takedown.
What is new. Silent Train is not a standing botnet. As lead researcher Michael Horka told CyberScoop, there is not one network to take down. According to the report, each session starts on rented cloud servers outside the United States, passes through hacked small office and home office (SOHO) routers and Internet of Things (IoT) devices in other countries, and then exits through a hacked device inside the United States so the traffic looks local. Operators could build a new chain in under two minutes, sessions averaged about four hours, and afterward they removed their tools and took the chain apart. The report counts more than 27 types of devices used this way. By early 2025, hacked business firewalls and servers were also being kept as longer-lived final hops for one to three months.
What they go after. Black Lotus Labs says Volt Typhoon focused on systems that already manage everything else: endpoint and network management platforms, software-defined wide area network (SD-WAN) controllers, and other central administration tools. One compromised management platform gives the reach of a full intrusion without moving through the network. The report names zero-day campaigns against Quest KACE (likely), Versa Director, N-able N-central (Common Vulnerabilities and Exposures entries CVE-2025-8875 and CVE-2025-8876), Cisco Catalyst SD-WAN (CVE-2026-20127) and VeloCloud Orchestrator (CVE-2026-16812). Hawaii, California and Texas were the most targeted states. Separately, Nextgov reports that Department of Energy facilities were targeted over the last year, according to a person with knowledge of the matter, and that multiple utilities have been dealing with Volt Typhoon issues, according to a former United States official. Neither claim is in the Lumen report.
Where this shows up from the plant floor to the cloud. The report does not describe attacks on controllers. It describes attacks on the systems around them. At a utility, the firewall, virtual private network (VPN) gateway or SD-WAN box at a remote pump station or substation is exactly the kind of edge device the report describes. In the control center, network monitoring and endpoint management servers often see and control both the business and operational technology (OT) networks. In the cloud and with outside providers, a managed service provider (MSP) or vendor portal with standing access into the plant is a trusted path in. Because the last hop is a hacked device inside the United States, the report says the traffic gets past blocking by country and by address reputation lists.
What it means for OT owners. If the attacker owns the tools your team uses to manage the network, normal-looking administrator activity is the attack. The question is which management systems can reach your OT network, who can log in to them, and whether you would notice if someone did.
What the Red Tiger team recommends:
Black Lotus Labs also points owners to the Cybersecurity and Infrastructure Security Agency (CISA) and the United Kingdom National Cyber Security Centre (NCSC) guidance on Volt Typhoon.
With 500+ assessments across critical infrastructure, the Red Tiger Security team helps owners map the management paths into OT with plant-safe methods, lock down remote access, and set up monitoring that can spot misuse of trusted tools.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources:
Black Lotus Labs (Lumen), "Silent Train: uncovering Volt Typhoon's operational framework for zero-day exploitation and strategic access," 28 October 2026: https://www.lumen.com/blog/en-us/silent-train-volt-typhoon-operational-framework
Nextgov/FCW, David DiMolfetta, 28 October 2026: https://www.nextgov.com/cybersecurity/2026/10/chinas-volt-typhoon-quietly-built-another-hacking-network-following-us-crackdown-new-findings-say/416848/
CyberScoop, Matt Kapko, 28 October 2026: https://cyberscoop.com/volt-typhoon-silent-train-covert-ephemeral-network-black-lotus-labs/
Check out our resources and book a follow-up call with our team.
