The Cybersecurity and Infrastructure Security Agency (CISA) published an industrial control system advisory on 3 November 2026 for PowerSYSTEM Center, software from Subnet Solutions of Canada that utilities and manufacturers use to manage substation and field devices such as protective relays. The advisory, ICSA-26-307-01, covers two flaws that let a person with an ordinary, low-privileged login do things only an administrator should be able to do. Both are rated 9.0 out of 10 on the Common Vulnerability Scoring System (CVSS). CISA says no known public exploitation has been reported and that the flaws are not exploitable remotely. Neither flaw is on the CISA Known Exploited Vulnerabilities (KEV) catalog. Fixed versions are available now.
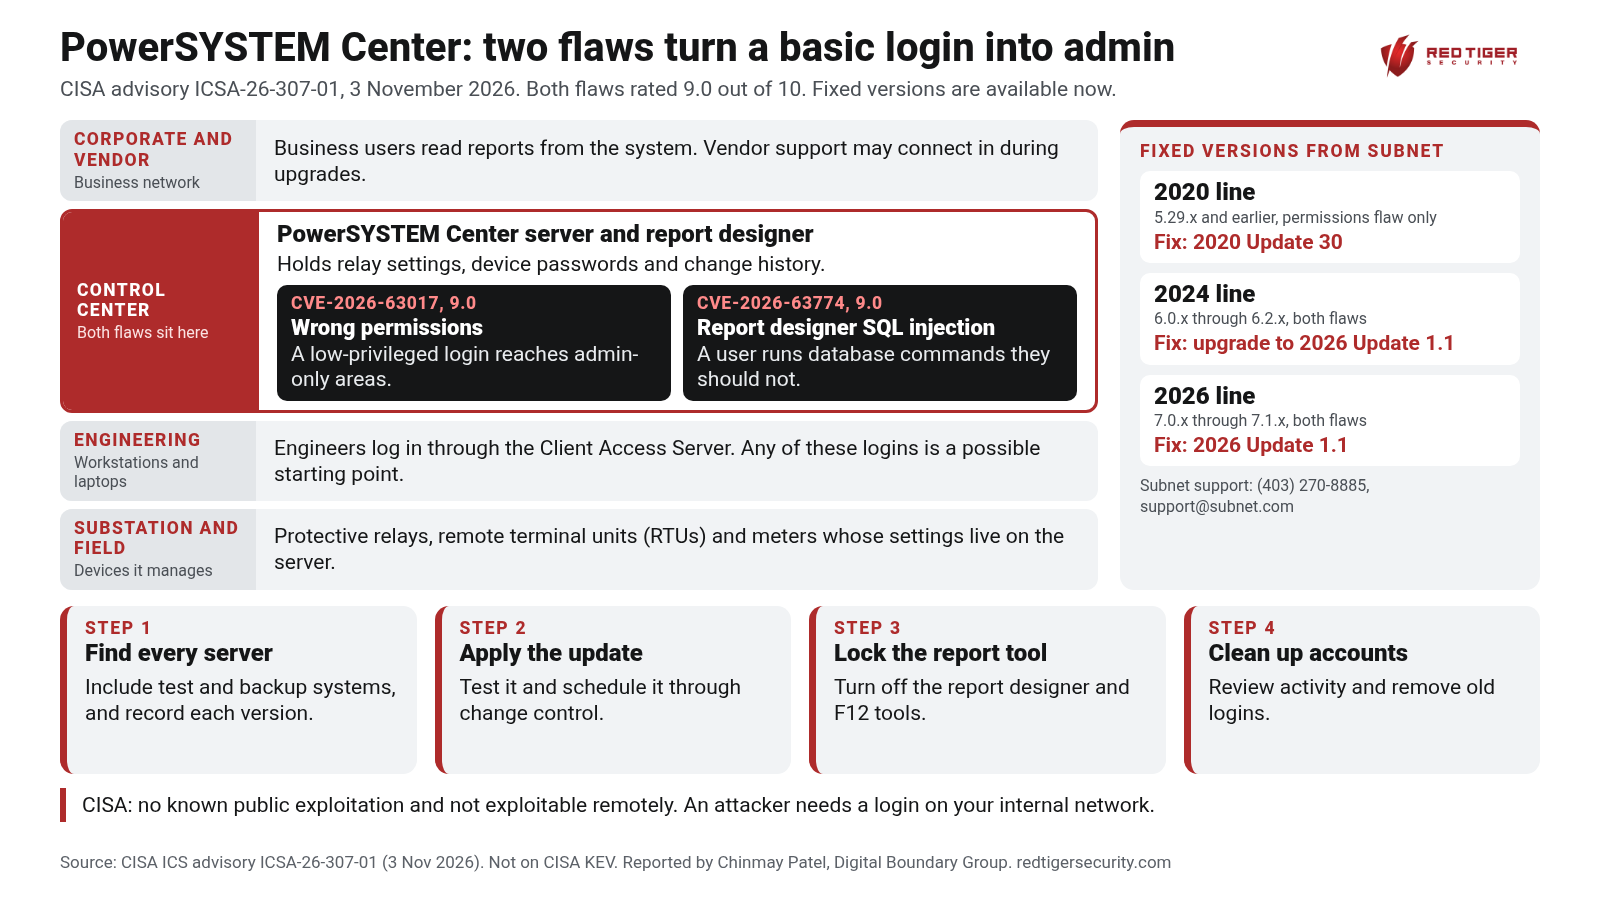
What the two flaws are. CVE-2026-63017 is an incorrect authorization flaw. A user who is logged in with a low-privileged account can reach parts of the application that are supposed to be limited to administrators. It affects PowerSYSTEM Center 2020 versions 5.29.x and earlier, PowerSYSTEM Center 2024 versions 6.0.x through 6.2.x, and PowerSYSTEM Center 2026 versions 7.0.x through 7.1.x. CVE-2026-63774 is a Structured Query Language (SQL) injection flaw in the report designer. SQL is the language the application uses to talk to its database, and injection means a user can slip their own database commands into a field that should only accept ordinary input. In this case a logged-in user can use the report designer to run database commands they are not allowed to run. It affects the 2024 and 2026 product lines. CISA credits Chinmay Patel of Digital Boundary Group and Subnet Solutions with reporting the flaws.
How an attacker would reach it. Both flaws need a valid login and access to the same network as the PowerSYSTEM Center server. CISA scores them as adjacent network attacks, which means the attacker has to be on a connected internal network rather than coming in from the internet. That lowers the risk, but it does not remove it. The realistic paths are an insider, a contractor or vendor account, or an ordinary user account whose password has been stolen.
Why this matters even without known attacks. A PowerSYSTEM Center server often holds the settings and the access passwords for the protective relays and other devices in a utility's substations. Protective relays are the devices that trip breakers to protect lines, transformers and people. If a low-privileged account can gain administrator rights, or read and change the database directly, it can reach that information. The server that manages the relays deserves the same care as the relays themselves.
Where it shows up from the plant floor to the cloud. In the field and in the substation, the protective relays, remote terminal units (RTUs) and meters are the devices PowerSYSTEM Center manages. In the control center, the PowerSYSTEM Center server and its database store device settings, passwords and change history, and the report designer runs reports against that database. Engineers and technicians reach the server from engineering workstations and laptops through the Client Access Server, the part of PowerSYSTEM Center that users log in to. Further up, reports from the system often go to corporate users, and vendor support may connect in during upgrades. Every one of those logins is a possible starting point.
What Subnet Solutions says to do. Users on the 2020 line should update to PowerSYSTEM Center 2020 Update 30. Users on the 2024 line should upgrade to PowerSYSTEM Center 2026 Update 1.1. Users on the 2026 line should update to PowerSYSTEM Center 2026 Update 1.1. The Subnet Solutions System Integration team and customer support team can help with upgrades at (403) 270-8885 or support@subnet.com. If you cannot update yet, Subnet Solutions recommends monitoring user activity records to make sure users are following the application's acceptable use policies, turning off Client Access Server users' access to the browser's F12 Developer Tools, and turning off user access to the report designer.
What the Red Tiger team recommends:
With 500+ plant-safe assessments across critical infrastructure, the Red Tiger Security team helps utilities find the systems that hold the keys to their field devices and close the paths into them.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources:
CISA, "Subnet Solutions PowerSYSTEM Center," ICS Advisory ICSA-26-307-01, 3 November 2026: https://www.cisa.gov/news-events/ics-advisories/icsa-26-307-01
CISA Common Security Advisory Framework (CSAF) file for ICSA-26-307-01: https://raw.githubusercontent.com/cisagov/CSAF/develop/csaf_files/OT/white/2026/icsa-26-307-01.json
Check out our resources and book a follow-up call with our team.