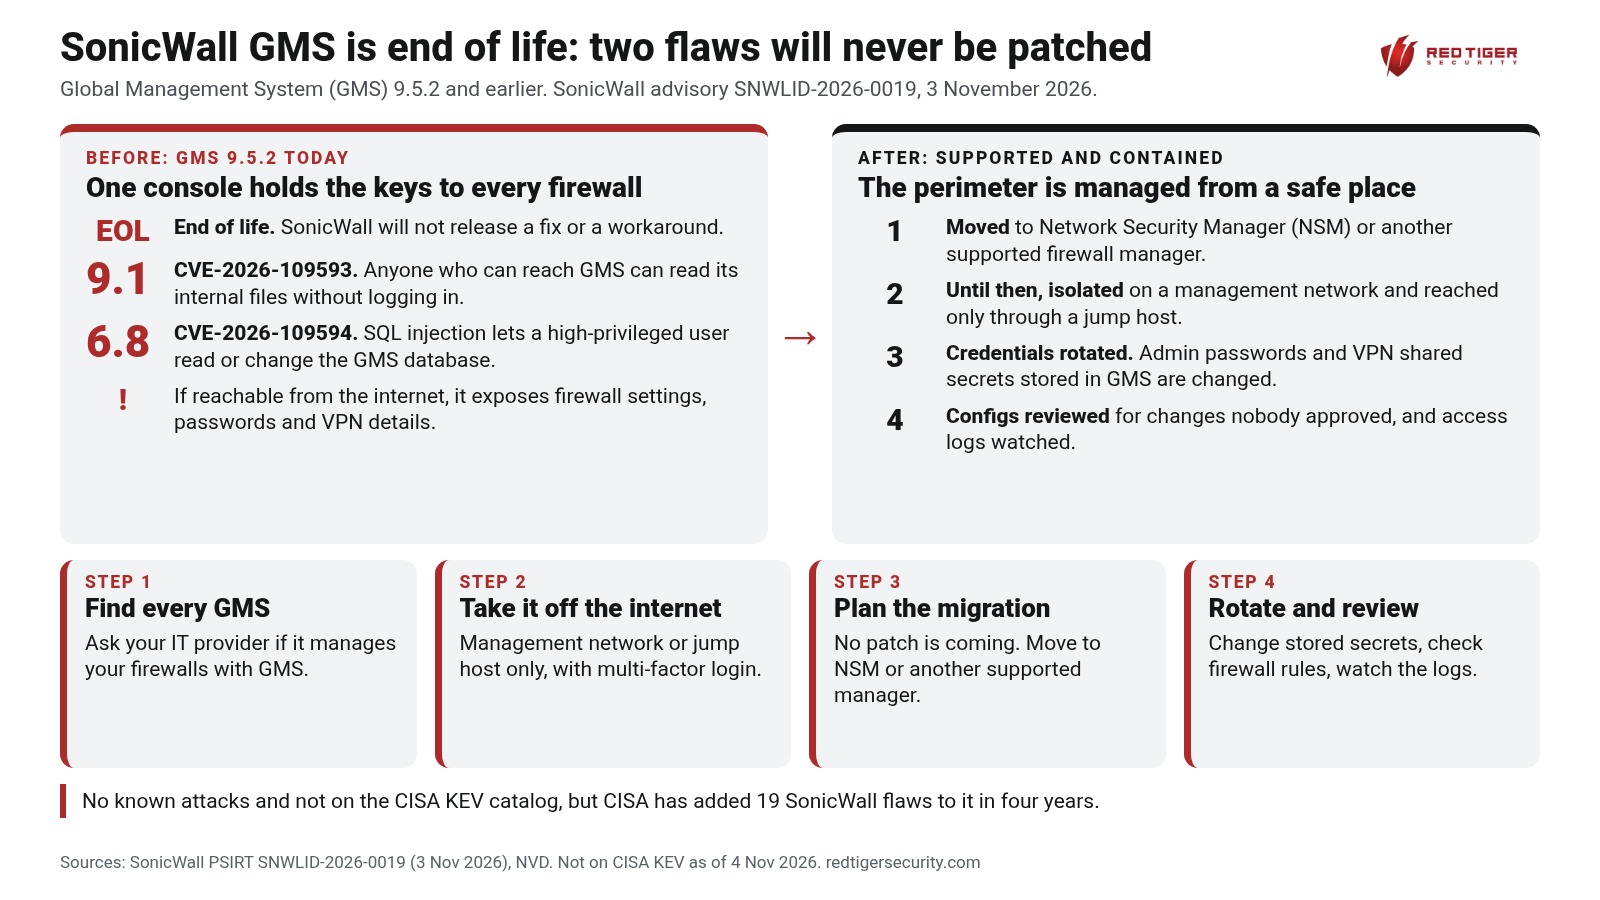
SonicWall has disclosed two vulnerabilities in its Global Management System (GMS), the software many organizations use to manage a fleet of SonicWall firewalls from one console, and has said it will not fix them. GMS version 9.5.2 and earlier has reached end of life, which means SonicWall no longer releases updates for it, including security fixes. SonicWall published its advisory, SNWLID-2026-0019, on 3 November 2026 and strongly encourages customers to upgrade to SonicWall Network Security Manager (NSM), its replacement management platform. As of 4 November, there are no reports of attacks using these flaws, and neither is on the Cybersecurity and Infrastructure Security Agency (CISA) Known Exploited Vulnerabilities (KEV) catalog. With no patch coming, the only real fixes are to move off GMS or to tightly limit who can reach it.
What the two flaws are. CVE-2026-109593 lets an attacker who can reach GMS over the network, without logging in, read internal GMS files and expose sensitive information. SonicWall and CISA both rate it 9.1 out of 10, critical, on the Common Vulnerability Scoring System (CVSS). CISA's assessment in the National Vulnerability Database (NVD) records no known exploitation but marks the flaw as automatable, which means an attacker could run it against many systems with simple scripts. CVE-2026-109594 is a SQL injection flaw. SQL, or Structured Query Language, is the language applications use to talk to their databases, and SQL injection means text entered into an application is passed to its database as a command, so an attacker can read or change records the application would normally protect. This one requires a logged-in user with high privileges, and SonicWall says that under specific conditions it could let that user access or modify information stored in the GMS database. SonicWall and CISA rate it 6.8 out of 10, medium. Both flaws affect the GMS virtual appliance and Windows versions 9.5.2 and earlier, and SonicWall lists no workaround. Researchers at Pentest-Tools.com reported both flaws.
Why an unpatched management server matters. GMS is not a single firewall. It is the console that configures many of them, so a GMS server can hold firewall configurations, administrator credentials, virtual private network (VPN) settings and the connection details for every device it manages. Reading its internal files could give an attacker what they need to reach the firewalls themselves. SonicWall products are also frequent targets. According to BleepingComputer, CISA has added 19 SonicWall vulnerabilities to the KEV catalog over the last four years, and 13 of them have been used by ransomware gangs.
Where GMS shows up from the plant floor to the cloud. SonicWall firewalls sit at the internet edge of many small utilities, water districts, manufacturing plants and remote sites, and sometimes between the business network and the control system network. Those firewalls are often installed and managed by an information technology (IT) provider or integrator, who may run GMS on its own server or in a hosted environment to manage many customers at once. That means the plant team may not know that GMS exists, which version it runs, or whether its web console can be reached from the internet. If GMS is exposed, the risk is not limited to one server, because the firewall rules and remote access settings that protect the plant perimeter are stored there.
What the Red Tiger team recommends:
With 500+ plant-safe assessments across critical infrastructure, the Red Tiger Security team helps owners find the management servers and edge devices that sit between the internet and their control systems and close the paths into them.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources:
SonicWall Product Security Incident Response Team (PSIRT), "End-of-Life (EOL) SonicWall GMS Multiple Vulnerabilities," SNWLID-2026-0019, 3 November 2026: https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2026-0019
NVD record for CVE-2026-109593: https://nvd.nist.gov/vuln/detail/CVE-2026-109593
NVD record for CVE-2026-109594: https://nvd.nist.gov/vuln/detail/CVE-2026-109594
BleepingComputer, "SonicWall warns of unpatched flaws in end-of-life GMS software," 4 November 2026: https://www.bleepingcomputer.com/news/security/sonicwall-warns-of-unpatched-flaws-in-end-of-life-gms-software/
Check out our resources and book a follow-up call with our team.