Attackers are now exploiting CVE-2026-58115, a critical flaw in Node-RED on Siemens SIMATIC IoT2050 Advanced gateways, and they are looking for any Node-RED editor left open without a password. Vulnerability intelligence firm VulnCheck reported that one of its decoy systems was successfully exploited on 30 October 2026, and that the same source sent 15 more attacks by 1 November. Some of those attacks left behind persistent webshells, which are hidden web pages that let an attacker come back later and run commands on the device.
What Node-RED is. Node-RED is a free, low-code programming tool. Engineers use a web browser editor to wire together small building blocks, called nodes, into a flow. A flow is a small program that might read values from a programmable logic controller (PLC), convert them to another protocol and send them to a historian or a cloud dashboard. Some built-in nodes can run operating system commands on the device itself, which is useful for engineers and dangerous in the wrong hands. The Node-RED project's own security guide states that by default the editor is not secured, so anyone who can reach its address can open it and deploy changes, and that this is only suitable on a trusted network.
What the flaw is. Siemens ProductCERT disclosed CVE-2026-58115 on 11 August 2026 in advisory SSA-834709. On SIMATIC IoT2050 Advanced devices running Industrial OS with Node-RED installed, the Node-RED HTTP interface does not require a login. Siemens says an unauthenticated remote attacker could create malicious flows and run code on the device with maximum privileges. Siemens rates it 10.0 out of 10, the highest possible score on the Common Vulnerability Scoring System (CVSS). The Cybersecurity and Infrastructure Security Agency (CISA) republished the Siemens advisory on 25 August as ICSA-26-237-03.
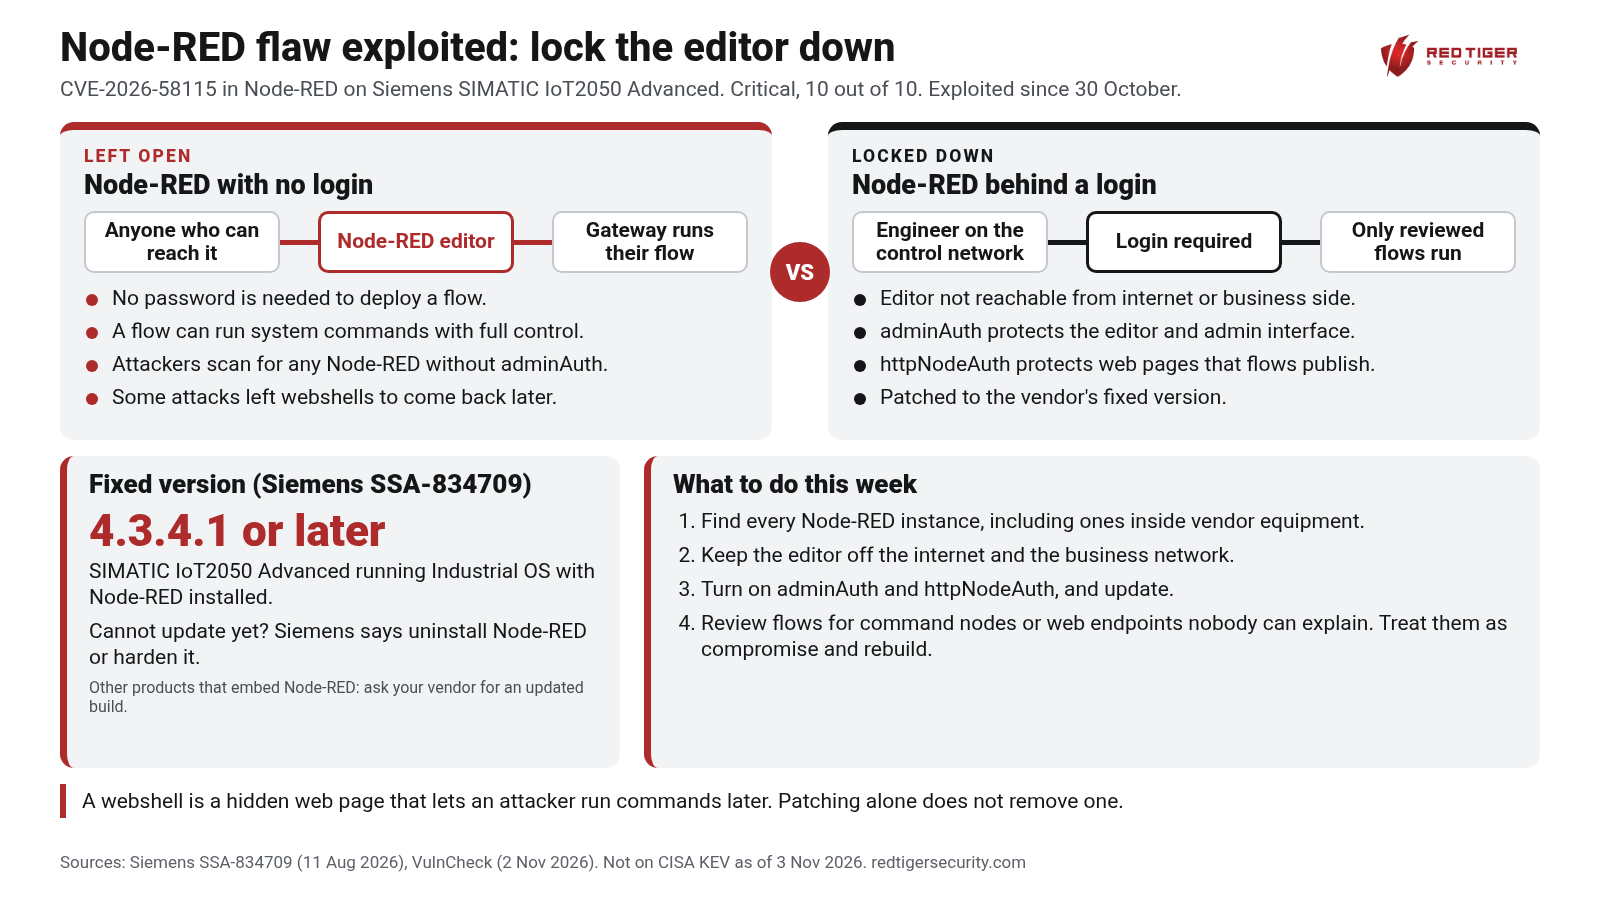
What attackers are doing. VulnCheck says the attackers scan for Node-RED instances that do not have adminAuth turned on. adminAuth is the Node-RED setting that requires a username and password for the editor and its administration interface. One web request is enough to deploy a flow that runs a command right away. The first payload VulnCheck saw was a bot program for Linux. VulnCheck did not analyze what the bot does. VulnCheck says the source looks like opportunistic mass scanning that also targets other software, not a campaign aimed at one company or one industry. It also notes that other automation vendors document using Node-RED, while saying it has not checked whether their products are affected.
Fixed version and current status. Siemens fixed the issue in SIMATIC IoT2050 Advanced version 4.3.4.1 and later. Where updating is not possible, Siemens lists two mitigations: uninstall Node-RED, or harden it by following the Node-RED user guide. As of 3 November 2026, CVE-2026-58115 is not on CISA's Known Exploited Vulnerabilities (KEV) catalog. VulnCheck has added it to its own exploited vulnerabilities list. We found no separate advisory or fixed release from the Node-RED project for this CVE. The project's guidance is its security guide: turn on adminAuth for the editor, turn on httpNodeAuth to require a password for web pages that flows publish, and use encrypted web access, known as HTTPS.
Where Node-RED shows up from the plant floor to the cloud. Node-RED is common in Industrial Internet of Things (IIoT) gateways such as the IoT2050, on edge computers next to the process, in protocol converters that bridge older field devices to newer systems, and in the data flows that move readings from the plant to a historian or cloud platform. It is also embedded inside products from automation and equipment vendors, so many sites run it without knowing. These boxes often sit on the control network with a second connection toward the business network or the internet. In our experience, integrators often install them during a project, leave the editor open for remote support and never come back to lock it down.
What the Red Tiger team recommends:
With 500+ plant-safe assessments across critical infrastructure, the Red Tiger Security team helps owners find the IIoT gateways and edge devices that never made it onto the asset list and close the paths into them.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources:
Siemens ProductCERT, "SSA-834709: Missing Authentication Vulnerability in Node-RED on SIMATIC IoT2050 Advanced with Industrial OS," 11 August 2026: https://cert-portal.siemens.com/productcert/html/ssa-834709.html
CISA ICS Advisory ICSA-26-237-03, Siemens SIMATIC IoT2050 Advanced, 25 August 2026: https://www.cisa.gov/news-events/ics-advisories/icsa-26-237-03
VulnCheck, "Exploitation Targeting Node-RED, a Tool Embedded in ICS Products," 2 November 2026: https://www.vulncheck.com/blog/exploitation-targeting-node-red
Node-RED, "Securing Node-RED": https://nodered.org/docs/user-guide/runtime/securing-node-red
NVD record for CVE-2026-58115: https://nvd.nist.gov/vuln/detail/CVE-2026-58115
Check out our resources and book a follow-up call with our team.