October 29, 2026

Hitachi Energy Fixes Flaws in CoreTec Transformer Monitors and TRO600 Wireless Mesh Routers

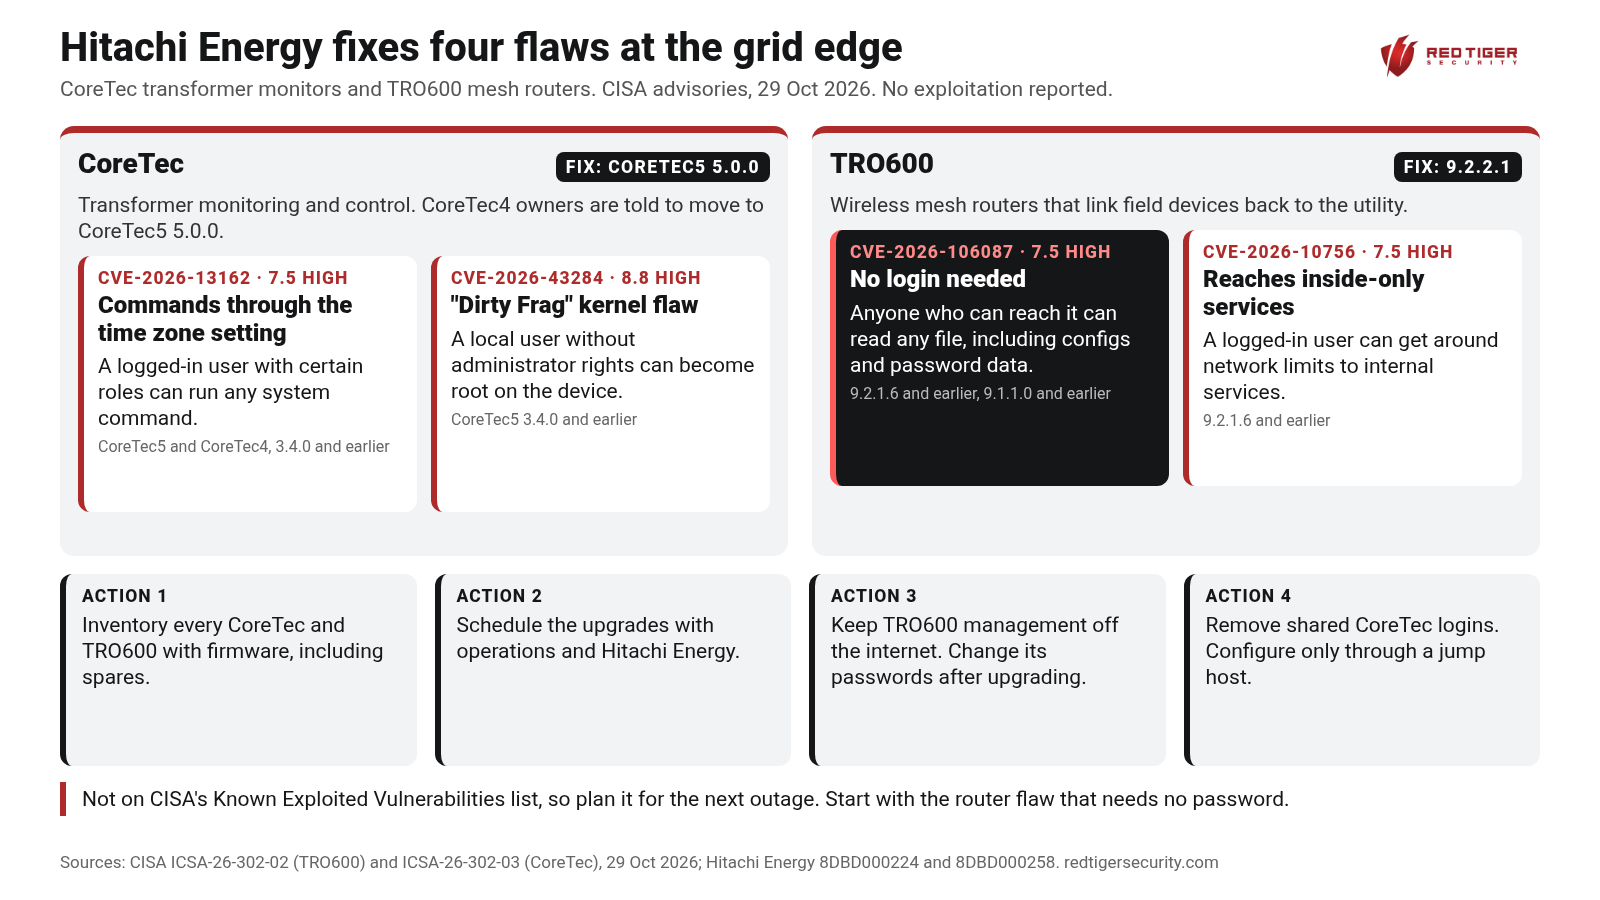
Hitachi Energy has fixed four vulnerabilities in two products that sit out in the electric grid: CoreTec, its transformer monitoring and control unit, and the TRO600 series of wireless mesh routers used to connect field equipment. The Cybersecurity and Infrastructure Security Agency (CISA) republished both Hitachi Energy advisories on 29 October 2026 (ICSA-26-302-02 and ICSA-26-302-03). Neither advisory reports exploitation, and none of the four flaws is in CISA's Known Exploited Vulnerabilities (KEV) catalog as of its 28 October release. That gives owners a planned window to fix them, rather than an emergency.

What Hitachi Energy reported

CoreTec (CISA advisory ICSA-26-302-03, Hitachi Energy advisory 8DBD000258):

  • CVE-2026-13162 is a command injection flaw, which means the device passes text a user typed straight into an operating system command. It sits in the part of the configuration service that sets the time zone. A logged-in user with certain roles can use it to run any system command with full control of the device. It scores 7.5 out of 10, High, on the Common Vulnerability Scoring System (CVSS) version 3.1. It affects CoreTec5 and CoreTec4 versions 3.4.0 and earlier.
  • CVE-2026-43284, which CISA's summary calls a "Dirty Frag" flaw, is in the Linux kernel inside CoreTec5. It lets a local user without administrator rights become root, the all-powerful account on the device, by abusing how the kernel decrypts IPsec packets, the encrypted network traffic used for secure tunnels. CVSS 3.1 score 8.8, High. It affects CoreTec5 versions 3.4.0 and earlier.
  • The fix is CoreTec5 version 5.0.0. For CoreTec4, Hitachi Energy's listed remedy is to upgrade to CoreTec5 version 5.0.0.

TRO600 (CISA advisory ICSA-26-302-02, Hitachi Energy advisory 8DBD000224):

  • CVE-2026-106087 lets someone with no login read or download any file on the router, including configuration files and password data. CVSS 3.1 score 7.5 (CVSS 4.0 score 8.7), High. It affects versions 9.2.1.6 and earlier and 9.1.1.0 and earlier.
  • CVE-2026-10756 lets a logged-in user get around network restrictions and reach services that are meant to be reachable only from inside the router itself, which can expose sensitive functions and information and disrupt the device. CVSS 3.1 score 7.5, High. It affects versions 9.2.1.6 and earlier.
  • The fix is version 9.2.2.1. Version 9.1.2.0 also fixes the file read flaw, but Hitachi Energy recommends the latest release, 9.2.2.1.

Hitachi Energy's own teams and Hitachi India's research center reported the flaws. CISA lists the energy sector and worldwide deployment for both products.

Why this matters on the plant floor and out in the field

A transformer monitor is not a back-office server. It watches the health of one of the most expensive and slowest-to-replace assets a utility or industrial plant owns, and its readings feed alarms and maintenance decisions. If someone gains full control of that device, the risk is that operators stop trusting, or never see, the readings that warn them a transformer is in trouble. The device is also often a path from the substation network back toward the operations center.

The TRO600 file read flaw worries the Red Tiger team most, because it needs no password. A mesh router that hands out its configuration and password data gives an attacker a map of the field network and, potentially, credentials that work on other devices if passwords are shared. Wireless field networks also tend to cover many remote sites with little physical supervision, so a weakness there is a weakness at every site.

Where it shows up, plant floor to cloud

At the field level, the TRO600 routers connect meters, reclosers, sensors and other field devices back to the utility. At the substation and plant level, CoreTec sits on the transformer and talks to the substation network and the supervisory control and data acquisition (SCADA) or asset health systems. Above that, the engineering workstations and remote access paths used to configure both products are where an attacker would most likely start, since both CoreTec flaws need a login first.

What owners should do now

  1. Find every CoreTec and TRO600 in your inventory, with its firmware version. Check spares and units that were installed by integrators or service contractors, which are often missing from the asset list.
  2. Plan the upgrades with operations and Hitachi Energy: TRO600 to version 9.2.2.1, and CoreTec5 to version 5.0.0. For CoreTec4 units, ask Hitachi Energy what the move to CoreTec5 version 5.0.0 means for your installed hardware and schedule it into the next maintenance outage.
  3. Until the routers are patched, make sure no TRO600 management interface can be reached from the internet or the business network, and treat its stored passwords as possibly exposed. Change them after upgrading and make sure they are not reused on other devices.
  4. Review who has accounts on CoreTec units and remove shared or unused logins, since both CoreTec flaws start with a logged-in user. Limit configuration access to named engineers coming through a controlled jump host, a single hardened server used for remote access.

Red Tiger Security has completed 500+ plant-safe operational technology (OT) assessments and trained 4,500+ engineers and operators. Our team can help you inventory field and substation devices, plan firmware upgrades without disrupting operations, and lock down remote access to the grid edge.

We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min

Sources
CISA ICSA-26-302-03, Hitachi Energy CoreTec: https://www.cisa.gov/news-events/ics-advisories/icsa-26-302-03
CISA ICSA-26-302-02, Hitachi Energy TRO600: https://www.cisa.gov/news-events/ics-advisories/icsa-26-302-02

‍

Cite this advisory: Red Tiger Security, "Hitachi Energy Fixes Flaws in CoreTec Transformer Monitors and TRO600 Wireless Mesh Routers", October 29, 2026, https://www.redtigersecurity.com/advisory/hitachi-energy-coretec-tro600

Read the original source →

We are here to help.

Check out our resources and book a follow-up call with our team.
