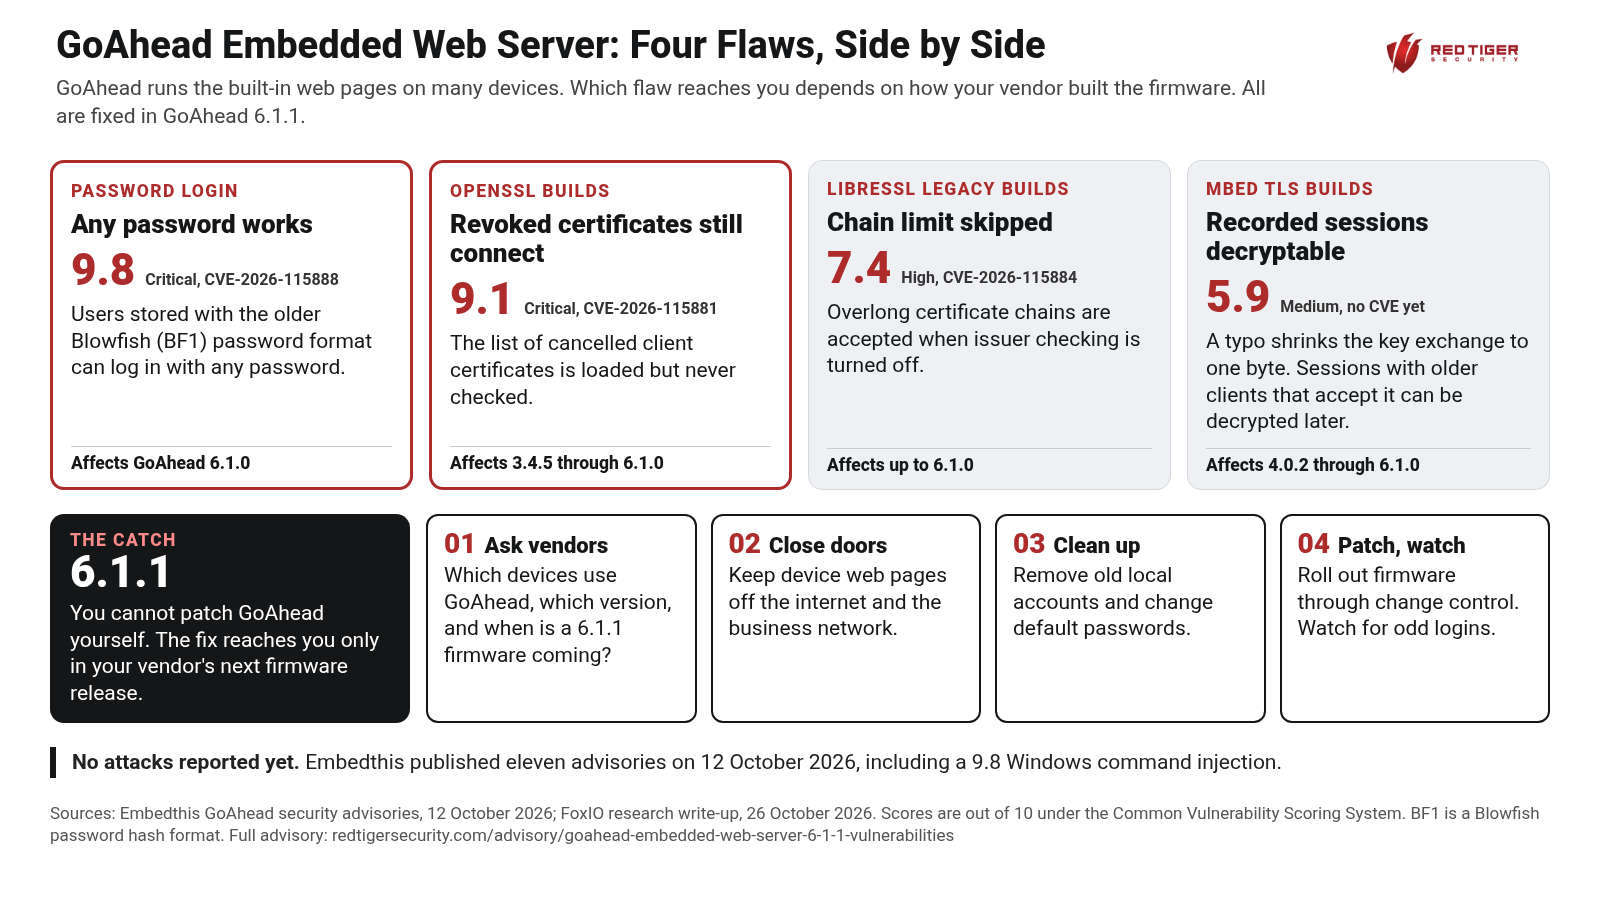
On 12 October 2026, Embedthis, the company that maintains the GoAhead embedded web server, published eleven security advisories, all fixed in GoAhead version 6.1.1. On 26 October 2026, researcher Sébastien Féry of the security firm FoxIO published a detailed write-up of three of them, and the story has spread quickly since. GoAhead is the small web server built into many devices so that people can manage them from a web browser. According to FoxIO, it runs in hundreds of millions of Internet of Things (IoT), firewall, operational technology (OT) and military devices, and FoxIO names Siemens, Rockwell, Honeywell, GE, Digi, Palo Alto Networks and others among the manufacturers that use it. No exploitation in attacks has been reported so far.
The catch is that you cannot patch GoAhead yourself. It is compiled into each manufacturer's firmware, so a device gets the fix when its manufacturer ships a new firmware release built on GoAhead 6.1.1. That is why the Red Tiger team is treating this as a vendor follow-up item for every plant.
What the most serious flaws do, according to the Embedthis advisories:
The other advisories cover web script argument and environment injection (CVE-2026-115880 and CVE-2026-115882), HTTP request smuggling, where a crafted request is read differently by two systems, a digest login flaw that leaks a server secret, and session fixation, where the login session ID is not changed after sign-in. All are fixed in 6.1.1.
Where GoAhead shows up, from the plant floor to the cloud: Look for it anywhere a device has a built-in web page for setup or status. On the plant floor that means programmable logic controller (PLC) communication modules, remote input and output racks, drives, protocol gateways and serial-to-Ethernet converters. In the network, it means industrial switches, routers, cellular modems and firewall management pages. In the control room and the building, it means uninterruptible power supplies, power distribution units, printers, cameras and building management controllers. At the edge, it means remote access appliances and cloud-connected gateways that technicians and vendors log in to from outside. Whether a given product uses GoAhead, and which version and encryption library it uses, is something only the manufacturer can confirm.
What the Red Tiger team recommends:
With 500+ assessments across critical infrastructure, the Red Tiger Security team helps owners build a plant-safe inventory of embedded components like GoAhead, chase vendors for fixed firmware, and lock down management access from the plant floor to the cloud.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources: Embedthis GoAhead security advisories, 12 October 2026: https://github.com/embedthis/goahead/security/advisories
FoxIO, "Choose Your Backend: Three TLS Bugs in GoAhead," 26 October 2026: https://foxio.io/blog/choose-your-backend-three-tls-bugs-in-goahead
GoAhead 6.1.1 release notes: https://github.com/embedthis/goahead/releases
Check out our resources and book a follow-up call with our team.
