The Cybersecurity and Infrastructure Security Agency (CISA) released its new strategy, "CISA 2030: Defend, Harden, Prevail," on 26 October 2026. It is a short roadmap for how the agency will focus its own work through 2030, and it names the security of operational technology (OT) as one of its key objectives. It is worth being clear about what this document is. It is a strategy, not a regulation. It does not create new legal requirements for asset owners, vendors or integrators. What it does is tell the industrial community where CISA plans to put its people and money, and that usually shapes the guidance, services and outreach that reach plants and utilities over the next few years.
What changed:
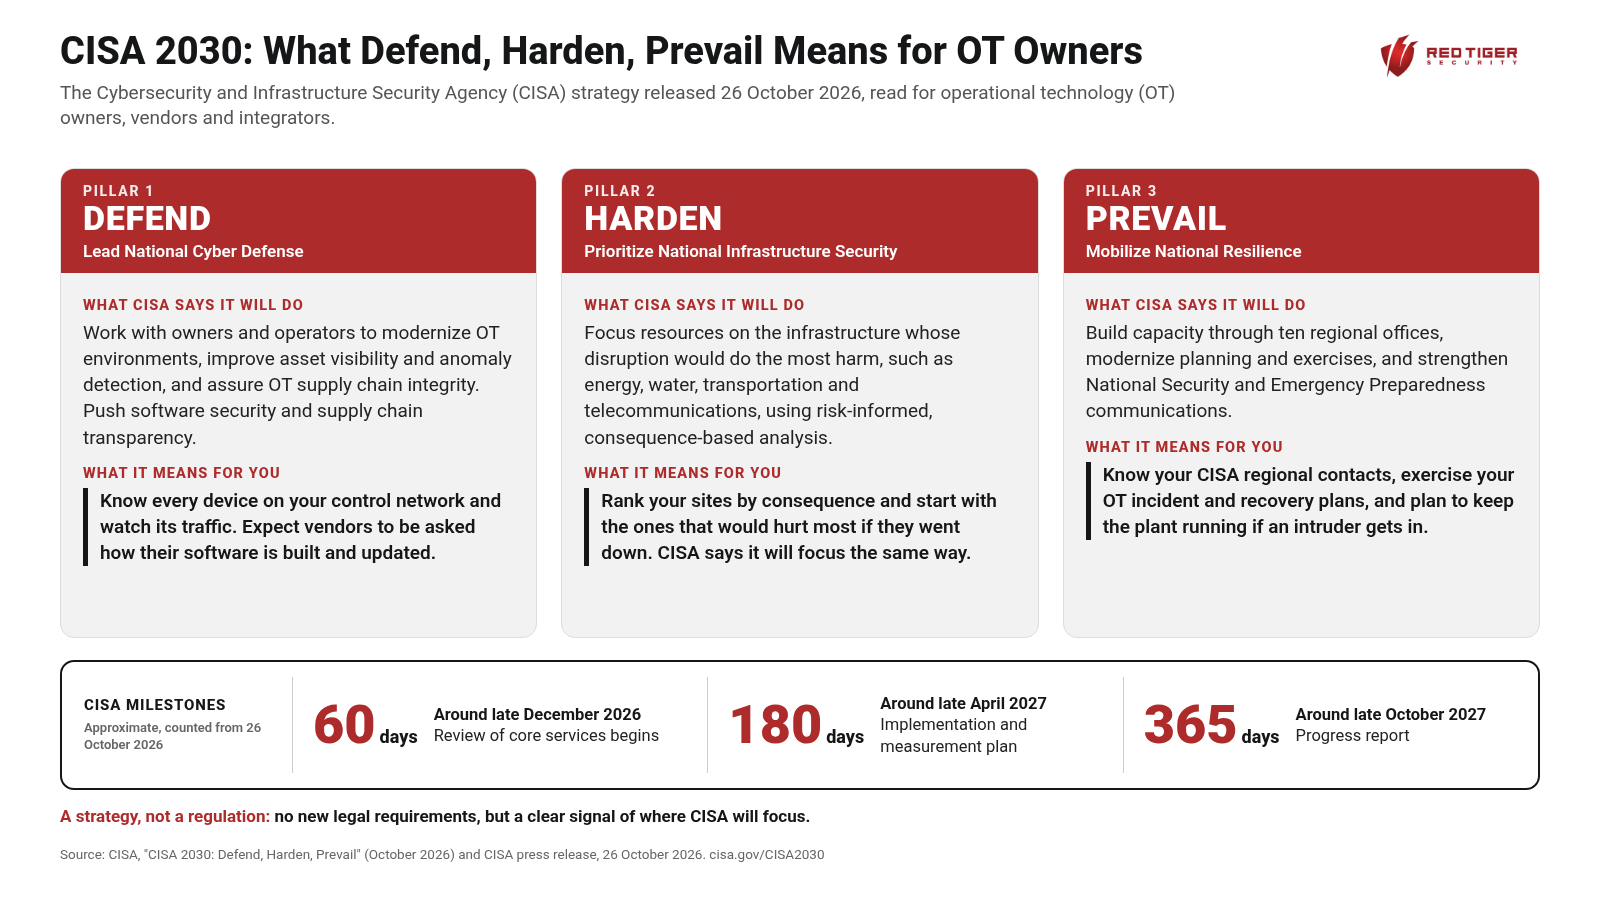
CISA organizes the strategy around three pillars.
Defend: Lead National Cyber Defense. CISA says it will work with government and industry partners to reduce cyber risk, disrupt malicious activity and secure new technologies. This is where operational technology shows up by name. According to the strategy, CISA will work alongside critical infrastructure owners and operators to modernize OT environments, improve asset visibility and anomaly detection, and assure the integrity of the OT supply chain. The same pillar commits CISA to data-driven guidance on software security and supply chain transparency, and to helping owners stay resilient against the threats that come with emerging technologies.
Harden: Prioritize National Infrastructure Security. CISA says it will focus its resources on the infrastructure whose disruption would do the most harm to public health and safety, the economy and national security, and it names energy, water, transportation and telecommunications as examples of essential services. The strategy says CISA will move away from broad "all-hazards" approaches toward risk-informed, consequence-based analysis, and will support the White House in developing a National Risk Register. It also calls for a faster path from intelligence to operations, so that threat information turns into alerts and action sooner.
Prevail: Mobilize National Resilience. CISA says it will build capacity through its ten regional offices, modernize its planning and exercise programs, and strengthen National Security and Emergency Preparedness communications, which keep government and public safety connected during a crisis.
Across all three pillars, CISA says it will move from a passive defense posture to an aggressive, anticipatory stance focused on finding and removing malicious access to critical infrastructure before it can be used. In his welcome letter, Acting Director Nick Andersen writes that there is no guarantee a strong defense will stop every intrusion, so the goal is to detect intruders quickly, evict them and keep critical operations running. In the press release, he calls on everyone from owners and operators to vendors and technology manufacturers to act now. CISA says the strategy advances the Cyber Strategy for America and the National Resilience Strategy.
Key dates (approximate, counted from the 26 October 2026 release):
Within 60 days, around late December 2026, CISA will begin a review of its core services and capabilities.
Within 180 days, around late April 2027, CISA will deliver a plan for carrying out the strategy and measuring the results.
Within 365 days, around late October 2027, CISA will report on its progress.
Who this affects:
Asset owners in water and wastewater, electric power, oil and gas, chemical, maritime and manufacturing should expect CISA's services and outreach to lean toward the facilities with the highest consequences if they go down. Equipment manufacturers and vendors are named directly in the call to action, and they will feel the attention on software security and OT supply chain integrity. System integrators and service providers should expect questions about their remote access and support connections, because those connections are often how an attacker gets a foothold in a plant.
Where this shows up from the plant floor to the cloud:
At the field level, asset visibility means knowing every controller, drive, safety system and network device that is actually on the network, along with its firmware version. In the control room and in the buffer network between business information technology (IT) and OT, anomaly detection means watching the traffic for behavior that does not belong there. At the enterprise and cloud level, the software security and supply chain work reaches into vendor cloud services, remote access portals and the software updates that flow down into the plant.
What the Red Tiger team recommends:
1. Build an accurate OT asset inventory. CISA's OT objective starts with asset visibility, and you cannot protect or monitor what you have not found. On live OT, a passive, plant-safe assessment is the safe way to build it.
2. Put monitoring where it counts. Add anomaly detection at the boundary between IT and OT and inside the control network, so an intruder who gets in is found and removed quickly, which is the outcome the strategy describes.
3. Ask your vendors and integrators direct questions. Find out how their software is built and updated, how their remote access into your plant is controlled, and what they can tell you about the components inside their products.
4. Rank your sites by consequence and put the dates on the calendar. Decide which facilities would cause the most harm if they went down and start there, then check back with CISA around late December 2026, late April 2027 and late October 2027 for the review, the implementation plan and the progress report.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Source: https://www.cisa.gov/news-events/news/cisa-unveils-new-strategy-strengthen-national-cyber-defense-and-critical-infrastructure-security
Check out our resources and book a follow-up call with our team.
