On 29 October 2026, a penetration tester published a write-up showing how he took over two Windows servers running AXIS Camera Station, the video management software (VMS) used to run Axis IP cameras, during an authorized test at a factory. From there he recovered the stored passwords for every camera those servers managed and logged in to the cameras directly. We are not repeating the technical steps here. What matters for plant owners is that every flaw he used has a vendor fix or workaround today.
The Red Tiger team is flagging this one because, in more than 500 assessments of industrial sites, we routinely find the camera system sitting on the same flat network as the business side, the control system side, or both.
What is affected
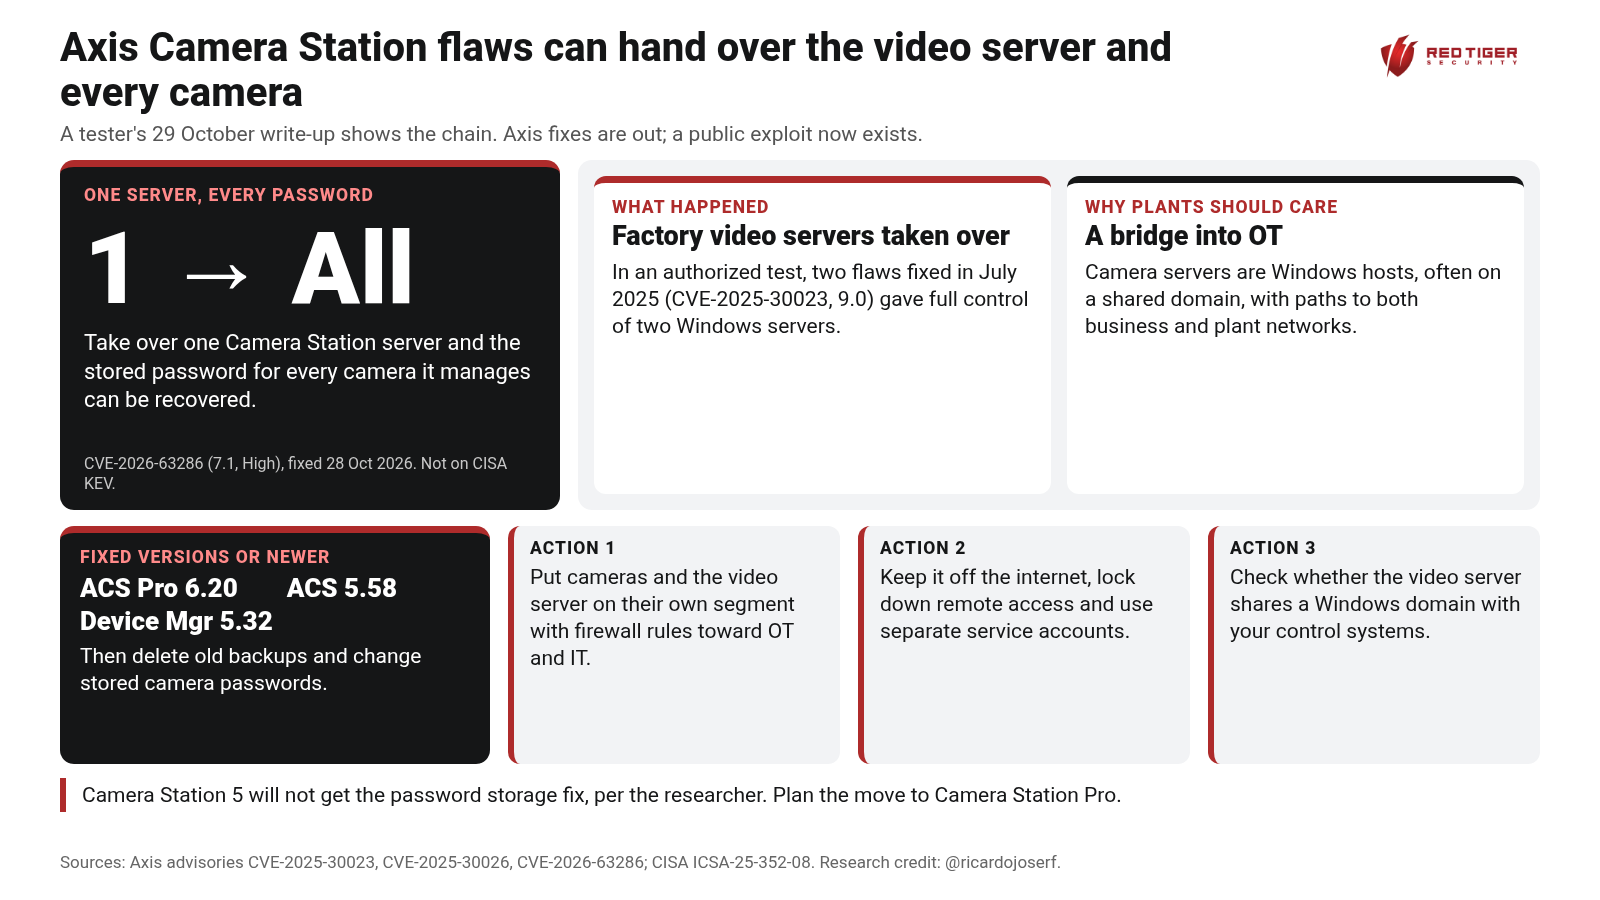
- CVE-2025-30023 (Axis score 9.0 out of 10, Critical): a flaw in how the Camera Station client and server talk to each other lets a logged-in user run code on the server. Affects AXIS Camera Station Pro before 6.9, AXIS Camera Station 5 before 5.58 and AXIS Device Manager before 5.32.
- CVE-2025-30026 (Axis score 5.3, Medium; the National Vulnerability Database (NVD) rates it 9.8, Critical): a way to skip the login on the Camera Station server. Affects Camera Station Pro before 6.9 and Camera Station 5 before 5.58. Combined with the first flaw, it means an attacker on the network does not need a password at all.
- CVE-2026-63286 (7.1, High): the way Camera Station protects stored device passwords and its database backups is weak enough to undo once someone has the files. Axis fixed it in Camera Station Pro 6.20 on 28 October 2026. Camera Station 5 will not get this fix, according to the researcher. Backups made before 6.20, including one the update itself creates, stay exposed until you delete them.
Both 2025 flaws were found by Claroty Team82 and fixed in July 2025, and the Cybersecurity and Infrastructure Security Agency (CISA) covered them in industrial control system advisory ICSA-25-352-08. Axis says it is not aware of attacks in the wild, and none of the three is in CISA's Known Exploited Vulnerabilities (KEV) catalog as of its 30 October release. A working public exploit now exists, so expect that to change.
Why plants should care
A camera server is not just a camera server. It is a Windows machine, often joined to a domain, that holds the passwords for every camera and sometimes email, file share and cloud account settings. It usually has a path to the business network for viewing and a path into the plant where the cameras sit. Take it over and an attacker gets full control of the server, every camera feed, and a foothold that may reach control systems. In this case, the tester reached the factory network that way.
What to do now
- Update AXIS Camera Station Pro to 6.20 or later. If you are still on AXIS Camera Station 5, update to 5.58 or later now and plan the move to Pro, since the password storage fix is Pro only. Update AXIS Device Manager to 5.32 or later.
- After updating, delete old Camera Station backups, including the one the update creates, and change every camera and device password stored in the system, as Axis advises.
- Put the cameras and the VMS server on their own network segment or virtual LAN (VLAN), with firewall rules that only allow the specific traffic needed toward the business network and none into the control system network unless there is a documented need.
- Make sure no Camera Station server or camera is reachable from the internet. Remove port forwarding, and remove or lock down remote access tools on the server. Use the plant's approved remote access path with multi-factor authentication.
- Run the VMS under its own service accounts, not shared or domain administrator accounts, and use unique camera passwords.
- Check whether the VMS server is joined to the same Windows domain as your control systems. If it is, treat it as part of the control system and harden it, or move it out of that domain.
- Monitor the VMS server: new local administrator accounts, unexpected processes started by the Camera Station service, and connections from unusual hosts to its client port.
We have trained more than 4,500 people on industrial cybersecurity, and segmenting the "non-control" systems like cameras is one of the most common gaps we help fix.
We are here to help, so check out our resources online at www.redtigersecurity.com and book a follow-up call with our team if you have any questions: https://calendly.com/jonathanpollet/30min
Sources: Axis CVE-2025-30023 advisory; Axis CVE-2025-30026 advisory; Axis CVE-2026-63286 advisory (28 October 2026); CISA ICSA-25-352-08; NVD CVE-2026-63286. Research credit: researcher @ricardojoserf